Category: Editorial

  • Finding a Balance

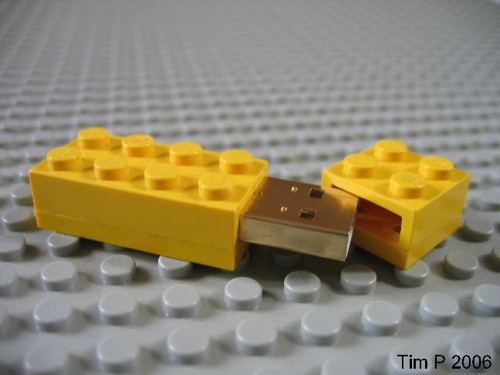
    lego USB
    Are devices like this a problem?

    This editorial was originally published on Nov 19, 2007. It is being republished as Steve is on vacation.

    When I started in IT things were much simpler. We had smaller data sets, but hardware was larger. There just wasn’t a good way to transfer large amounts of data on 3 1/2″ floppy drives. I remember CDs coming into being and CD writers became a concern, but since few people had them and we knew who they were, it wasn’t a big problem. The zip drives created a cause for concern briefly with their 100MB capacity, but again, they were somewhat bulky and easy to spot.

    However with the growing sizes of flash drives, storage in cell phones, and the monstrous capacity of iPods and other music players, it seems that data has little chance of being contained by IT within the walls of the organization.

    I saw an interesting discussion about managing all these technology devices and the problems that come with so much storage being in reach for so many people.

    So we’re data people, we get beat up to ensure our SOX procedures work well, and we’re in the trenches. With that in mind, the poll this week is…

    Does it make sense to ban personal storage devices?

    I know it’s not practical to actually try and prevent the iPods and other devices from coming into the building. You for sure cannot take away all the cell phones from people. But does it make sense to prevent these devices from connecting to your network? Ban USB and Bluetooth; don’t purchase rewriteable drives except for admins who can be monitored. Some other ideas?

    That might not even work. Recently a report surfaced about some executives in Korea that stole nearly $2billion worth of trade secrets with USB drives and taking them to a new company.

    Think about the past experiences we”ve had. Suppose you”d locked down floppy drives and CD burners a decade ago. All of a sudden MP3 players appear and get mounted as removable drives. It”s a new twist you hadn”t considered, so you shut down all the serial, parallel, and USB ports. You get a new laptop and realize Bluetooth is now available and works just as well and your controls have been circumvented again. What do you do now? It’s a tough balance to strike. Are you trying to be a control freak and make it an hostile work environment or do you trust your employees and deal with the occasional problems that come with them?

    I’m not sure what the best solution is, but I’d venture to guess that banning the technologies won”t work. Someone will always come up with a new way to get around your controls, and more importantly, you won”t be as vigilant if the controls “appear” to work.

    I’d adopt the Counterpane approach to security, which is what security expert Bruce Schneier believes in. Assume you”ll get compromised and attacked and put systems in place to detect and respond to issues rather than trying to prevent all attacks.

    Steve Jones


    The Voice of the DBA Podcasts

    Everyday Jones

    The podcast feeds are now available atsqlservercentral.podshow.com to get better bandwidth and maybe a little more exposure :). We’ve upped the quality a little on the Quicktime files, so if it’s better from your side, let us know. Comments are definitely appreciated and wanted, and you can get feeds from there.

    The RSS Feed:  or now on iTunes! 

  • The Personal Checksum

    checksum
    Do you create a checksum for yourself?

    This editorial was originally published on Nov 2, 2007. It is being republished as Steve is on vacation.

    Someone sent me this article on foiling thieves in restaurants with a personal checksum. It’s an interesting idea and while it could help, I’m sure there are some smart people that will find a way around it.

    I don’t reconcile my restaurant bills that closely, but I have an idea of what I’ve spent and I think that changing of bills rarely happens. I spent about 8 years in the restaurant business cooking, waiting tables, bartending, and managing at various times. I worked in all types of restaurants from diners to nightclubs and I’ve rarely seen anyone change a tab. It does happen, usually when someone is upset about their gratuity. But the person usually will brag about it to other employees and often you can tell when a ticket is changed.

    I don’t condone that behavior. If someone doesn’t want to tip you, then they don’t have to. On the other hand, if you’re going out to a restaurant in the US, remember that those people work essentially for tips. They aren’t paid minimum wage; they’re paid less as an allowance against tips.

    I’m not looking to start a restaurant debate, but with this being a Friday, I needed a poll and here it is:

    What other useful personal checksums do you use?

    Or do you need? Or do you wish someone would develop? Do you want some type of checksum on your credit score, something to tell you if it’s been accessed or even correctly calculated? Does it make sense to have some type of calculation to determine if your mortgage is being correctly credited?

    I’m not really sure what checksum I’d be looking for. To date I’ve had fairly good luck with security in my personal data and have had no real cause for concern.

    The one interesting thing I would like is a way to get a quick checksum for the last month off my automatic toll transponder and compare that to some calculation against my bill. I can never remember how often I’ve used it during the previous month.

    Steve Jones


    The Voice of the DBA Podcasts

    Everyday Jones

    The podcast feeds are now available atsqlservercentral.podshow.comto get better bandwidth and maybe a little more exposure :). Comments are definitely appreciated and wanted, and you can get feeds from there.

  • Watch Your Mouth

    It’s one way to control what you say

    I give a talk on branding and resumes that has been well received over the last few years. In it I cover the ways in which you can use networking, blogging, and other ways to improve the chances that employers will want to hire you. There are lots of jobs available, and lots of candidates, but finding a good fit is hard. I would argue that disclosing more about yourself, and your interests, is a good way to help find a good fit with an organization.

    One of the cautions I raise in my presentation is that you should be aware of how you present yourself, and the impressions you make. There are no right or wrong ways to do this, but there are ways that reflect differently on you to different people. As such, I do urge you to think about the implications of your actions, your posts, and the way in which you communicate with others. If you are looking for a job, it doesn’t make sense to unnecessarily restrict your options because of the things you say or write.

    I ran across this slide show on profanity and cursing at work. I’m not offended by off color language, but some people are, and they often won’t let you know that you’ve created a poor impression. If the data is accurate, the majority of people think regular cursing creates a negative impression. Whether you think it’s a lack of control, unprofessional, or anything else, it still is a negative impression. It’s also one of the things that caused some HR groups to eliminate candidates.

    These days there is competition for jobs, and if you find the job you really like, do you want to diminish your chances because of a few colorful words? You have the freedom in the US to say what you want, and I support that, but you also get the responsibility of handling the consequences. I’d argue a few colorful words aren’t worth giving someone a reason to choose another equally qualified candidate over you?

    Steve Jones


    The Voice of the DBA Podcasts

    We publish three versions of the podcast each day for you to enjoy.

  • Shadow IT

    shadow
    Do you have shadow IT in your organization?

    When I started working as a system administrator over 20 years ago, I worked for a central IT department at a remote facility for our company. Four of us managed a network of 1,000 nodes, with multiple servers under a boss that decreed we needed to respond quickly and effectively to requests made by clients. They came to us often, expecting results, and we delivered. I assumed all IT groups worked like this. Almost a year later I worked at another facility and was quite surprised to find a different situation.

    In the other location there were also four people and 1,000 nodes, but the IT group only managed around three quarters of those nodes. Different groups had their own servers and applications they managed. There were machines under desks in one department, where the desk’s owner was tasked with working half his time on department work, and half his time on technology issues. I only found out about this when one of them asked me how to solve a few problems; I then realized he was managing his own IT services for his group.

    Shadow IT is still around, and in some cases it’s growing. That can be a problem, not only for IT staffs who have less demand for services, and thus staff, but also for the security and data integrity of an organization. Someone managing IT operations part time may not understand the security or data issues they create, face, or just may not have time to deal with. They also won’t necessarily have the experience to work efficiently and effectively on administrative needs, though I know a central IT staff will necessarily do a better job.

    As a data professional I get concerned about Shadow IT groups, which might hoard their data, or even keep around data that’s gotten stale. I worry they’ll lose systems and then come to me for a solution to recover the data, often without having managed backups. Most importantly, I worry they’ll make a mistake, cause a business problem, and not only will I need to clean up the mess, I’ll share in the blame for not helping them build something they needed in the first place.

    Shadow IT is usually the result of a non-responsive central group. I’ve always made it a point to try and help people get the tools they need to work. Sometimes blanket policies prevent this from happening, but by making friends I can usually get Shadow IT people to consult with me and listen to suggestions and ideas. It isn’t perfect, but if I can get them to make regular backups, it’s a win.

    Steve Jones


    The Voice of the DBA Podcasts

    We publish three versions of the podcast each day for you to enjoy.