Category: Editorial

  • Hacking the Admin

    Recently Twitter had a security breach, with a silly scam. At least, I’d think it was silly. I saw a tweet from Elon Musk noting that he’d return $2k in bitcoin for every $1k anyone sent to him. He was feeling generous.

    While that might seem silly, a number of other high profile accounts were breached and seemed to lend some level of veracity to the offer. I saw a few news reports that the hackers made off with over US$100,000, so apparently at least a few people were fooled. Twitter locked down verified accounts for a bit while it investigated, removed some tweets, and tried to close the security hole.

    What is disturbing here is that apparently the hack took place through Twitter syadmins, with privileged accounts. As of this writing, it isn’t clear if this was social engineering or a sysadmin worked with hackers, but there were internal tools allowing Twitter employees to post tweets on behalf of users.

    I have no idea how this happened, but I’m assuming this is some sort of data change made to their system. If this were an RDBMS with a “tweets” table, this would be adding a row to the table with links to the verified accounts’ linkage. Not a hard change in the SQL Server world, and certainly the type of change that most admins could make.

    The question might be should they be allowed? Many of us have made ad hoc data changes to systems to correct an issue, and some of us do this regularly.

    This reminds me of some customers whose DBAs aren’t allowed to directly connect from SSMS (or other clients) to production and make changes. All changes, including ad hoc data changes, must be submitted to some sort of pipeline, where the change is logged, and perhaps approved by someone else. A different sort of two factor authentication.

    Should this be a more common pattern of access to production systems? Limiting access by everyone, even admins? I know we need to trust administrators, but what happens when administrators get fooled by social engineering? A thorny attack vector that we ought to be considering in our architectures.

    Steve Jones
    Listen to the podcast at Libsyn, Stitcher or iTunes.

  • Adapting Privacy

    Lawyers will be lawyers.

    That’s a quote from a piece at Ars Technica on how and why search engine startup Neeva changed their privacy policy. Their business model relied on users paying Neeva to keep their data private. The goal being a secure platform that considered users privacy. An admirable goal, and one that I might have been welling to fund. There is a lot of data out there, and while I don’t mind companies improving their service to me with data about me, I don’t like them sharing it.

    In this case, Neeva didn’t read their terms of service very well. I don’t think this was malicious, but it was a mistake. I’m sure they used a legal group that someone recommended to them, and the lawyers were trying to craft a document that was structured to protect the company and allow for flexibility. Sharing data with affiliates and advertisers would seem to go against their model, but it’s something lawyers might think is fine. If you read the article, you can see how Neeva has adjusted their terms.

    As the world grows more digital, and we all deal with an ever increasing number of organizations, data privacy will become more important to some, perhaps many people. The ideas of reducing data retention, limiting transfer of data, and giving users more control is an idea that may take hold, especially if a few companies start to succeed with this business model. We’ve seen pressure on companies throughout this year cause them to shift their previous stances, sometimes dramatically.

    For those of us that work with data, this might mean easier administration in some ways. Certainly we will have to alter our systems for archival or more flexibly data retention policies. We might even need to adapt our data models to include more fields that allow us to easily decide what data to keep, remove, or obfuscate things.

    In fact, I wonder if that’s the future of privacy. We de-link old users by randomly setting values for PII data and keeping other information like sales values or URLs clicked as useful information for aggregation without any risk of disclosure.

    Steve Jones

    Listen to the podcast at Libsyn, Stitcher or iTunes.

  • A Dedicated Space

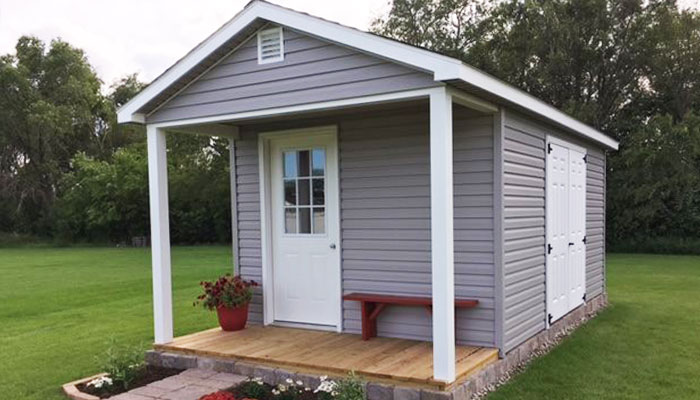
    Years ago I had a friend that was starting a consulting business. This person had worked for various organizations over the years and was ready to run a solo business. The city where this person resided was somewhat expensive, so they decided to convert a garden shed into an office space. They followed a similar process to this one, adding some interior finishing and electricity.

    This individual struggled to work alone in this space, after years of working in offices. While it provided separation from children and other home distractions, it was hard to get used to working alone the majority of the time. Eventually the moved their office back into the house.

    I was reminded of this when I saw a tweet from David Perell, noting that a good business model might be building recyclable, transportable offices. This pandemic has changed the way many people work, and while some have offices, I’ve had many of my colleagues working in bedrooms, dining rooms, and even in part of a kitchen area.

    The way we work has changed for much of the technology world and plenty of us have adapted well. People that hated being stuck at home with distractions are growing used to the idea, though I suspect that not having a permanent space of your own is likely growing old. I wonder how many people would like a shed like structure in their yard or garden, with about 100sq ft/9sq m of personal room for your desk and whatever you need for your job. There are some really small, neat designs with lots of windows, porches, even fancy designs. Interiors can be simple or designed just for you.

    Would any of you want to give up a little garden space to get a private office? With the changing world, and the chance that you might work at home for a long time, perhaps some of you would like a private space that’s just your own, perhaps even one that you could take with you if you moved to a new residence. Or maybe one that you can take to a shared space in a town. I could even see pods like this in an office park. Instead of a shared office space, maybe there would be outdoor pods near each other, where we can work near each other, but still in a safe, private way when we need to do so. Perhaps this is the next evolution of BYOD, as a Bring-Your-Own-Office.

    Steve Jones

  • Digging Into Internals

    Hugo Kornelis is a fellow Data Platform MVP and friend. He runs SQL Server Fast, and we recently put up an interesting page with this title: Debugging with debugger: investigating SQL Server’s internal structures. That’s a great title, and it is for a presentation that he is building and getting ready to present. I suspect it will be at a virtual conference soon, but we’ll see.

    Hugo digs deep into the details of how things work. If you read his blog regularly, you’ll learn a lot about the ways in which SQL Server processes queries. You should learn how to better tune your own queries and produce efficient code. At least that’s the goal.

    However, I wonder if most of you feel that way. While I see performance tuning sessions are often being the most popular topics at events, are you interested in internals? Do you actually use information from posts and presentations to dig in deeper to the way your queries are compiled and executed?

    I know Plan Explorer is a very popular tool among MVPs, and lots of people download it, but I still see so many basic questions on execution plans, I sometimes wonder if people are really using the tool to change they way they write code.

    If you want to learn more about query tuning, Hugo, Grant Fritchey, Aaron Bertrand, Paul White, Erik Darling, and many others will try to teach you. Just be sure you try and use the knowledge they impart in your daily work.

    Steve Jones