Category: Editorial

  • The Command Shell

    Security holes are all around. Are there any in xp_cmdshell?
    Security holes are all around. Are there any in xp_cmdshell?

    Recently I heard a few people arguing over the use of xp_cmdshell in a particular situation. One person was adamant that there was a security risk in using this feature. Many of you probably feel the same way, and even the SQL Server platform has recognized there could be dangers with this feature and has it disabled by default, as part of the secure by default installation.

    However the security around this procedure has been improved over the years. Non system administrators cannot execute xp_cmdshell by default. Administrators can open up access using a proxy account, but this requires specific configuration changes by administrators. This means that a lot of the danger of using xp_cmdshell for administrative tasks has been removed.

    Or has it? This Friday I wanted to poll you and find out what you think. Many of you are creative in how you use SQL Server and will think of possibilities that many of us would not consider.

    Is there a security risk in allowing xp_cmdshell to be used by members of the sysadmin role?

    I’m not looking for potential issues if a proxy account exists. Instead I’m asking if there are real dangers in allowing administrators to use this tool? I assume you trust your administrators and they will not maliciously use this tool to cause issues in your SQL Server. Let us know how you feel this week.

    Steve Jones


    The Voice of the DBA Podcasts

    We publish three versions of the podcast each day for you to enjoy.

  • What Do You Want to Know About I/O?

    Hope to see you at the conference.
    Hope to see you at the conference.

    There’s lots I want to know. What affect does an SSD have if I use it for a log file? One of my filegroups with indexes? What about tempdb? How do you dig in and prove latency to the storage groups from within SQL Server? Will the query optimizer take advantage of information about drive performance? There are lots of questions I have, and I’m hoping to get answers. I’m hoping to attend the “Ask Anything I/O” panel at SQL Intersection in a few weeks. I’m leaving the event Wed night, so unless there’s someone I’m trying to catch in a last minute meeting, I’ll be sitting in the audience.

    I am guessing that Brent Ozar, Kevin Farlee, and Mat Young will have lots of answers for me and others. I’m also guessing most of the questions will be met with references that are already out there, and I hope that the presenters will publish a list of questions and answers for attendees. That’s fine, as there are lots of times when I’m looking for information that has been published, but I can’t find in the ocean of Google results. Attending a session given by experts can be a way to shortcut some research and searching to find where the answers are located.

    That’s one of the reasons to attend a conference. Getting quick answers from experts, or learning how to better target your research. All the speakers at SQL Intersection are well known, longtime, expert SQL Server users who are friendly. They’re more than willing to answer questions, or help guide you to solve a problem or learn something new.

    The other great thing about conferences? You get to hear some great questions from other attendees. We all attack problems differently, and work in very diverse environments. There are many times I’ve heard how another person has implemented SQL Server and it’s intrigued, or even inspired, me to try something similar with my instances.

    If you can find the funding, SQL Intersection is a great event to attend, with an impressive list of speakers, each hand picked by Kimberly Tripp and Paul Randal of SQLskills. They provide amazing training in their Immersion events, and are trying to bring even more options to you with SQL Intersection. You can even walk away with something tangible in addition to all the knowledge you’ll gain: a Surface Tablet.

    Steve Jones


    The Voice of the DBA Podcasts

    We publish three versions of the podcast each day for you to enjoy.

  • A Good Security Response

    I'm glad Evernote acted quickly and decisively with this incident.
    I’m glad Evernote acted quickly and decisively with this incident.

    Security will become more and more important in the future, at least in my mind. As we become more interconnected and dependent on digital services, if the level of fraud and security failures do not fall, many people will hesitate to use these services. I think certificates will be the future of digital security, but until we get better support for managing them built into all our OSes, I’m not sure we’ll move beyond passwords. I do think we need to move past passwords, but we’re stuck with them for now.

    Recently Evernote had a security breach and they forced all users to reset their passwords. It was slightly annoying, but it was a comforting response for me. Two week after the incident I had to change the password on my iPad, which I rarely use. It was ironic since I was working on this particular piece when I reset my password.

    I wasn’t the only one that thought this was a good response. In this article from Enterprise Security, a number of security professionals praised the way Evernote handled this incident. They note that Evernote had implemented good security practices (from what we know) and notified people immediately. I certainly appreciate Evernote moving quickly on this and am glad I had to deal with the annoying password change. I don’t use the same password on other sites, and this was a good reminder to me that I shouldn’t. It also served as a reminder to tell my family to do the same thing.

    I’m not sure any company I’ve worked for would handle things this way. I haven’t had many security incidents at my previous employers, but I know in one case we were told not to disclose anything and fix issues. I’d like to think that most companies would disclose this, and I do think they should, but most wouldn’t. These things happen, just like break-ins happen in physical buildings. Companies should accept that, diagnose the issues, repair them, and move on. Customers will understand the problem and remediation steps. What customers don’t understand, or accept, is a company failing to inform them. Or failing to improve security when they know there are issues.

    Steve Jones


    The Voice of the DBA Podcasts

    We publish three versions of the podcast each day for you to enjoy.

  • Car Data

    I don't know if I like this layout, but I like more data being available from my car usage.
    I don’t know if I like this layout, but I like more data being available from my car usage.

    I really like cars. In my lifetime I have owned more than my share of vehicles, and I always look forward to renting new makes and models when I travel, just to drive something different. As cars have evolved over the last few decades, there are some things about the changes I love, and some things I dislike. Personally I like the idea of a key fob that enables me to unlock the car and start the engine with a button without pulling the keys out of my pocket. However, as someone that’s lost my share of keys, I’d prefer a real key as a backup mechanism. Unfortunately that doesn’t seem to be an option many manufacturers want to provide. I dread having to replace a $200 “smart key” at some point in order to drive my car.

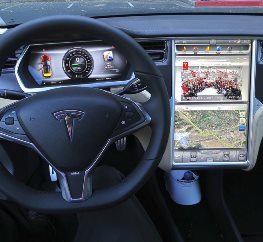
    Cars have implemented a wide array of technology over time, some of which drivers are not even aware. These days cars gather an impressive amount of data, though probably not quite at the scale of the new Dreamliner. Or maybe they do. According to this article, cars can produce “hundreds of MB/s” in data acquisition. I would guess most of that data is thrown away, but some may not. I was quite impressed with the amount of data Tesla logged during the recent test drive controversy with one of their vehicles.

    All this data, and the potential need to manage it, mine it, and perhaps make it available to other applications, is another sign of just how important our jobs as data professionals may be in the future. More and more of the things we encounter on a daily basis are creating data that we may turn into information for business decisions through creative uses of software. While some parts of our database systems may become easier to use, I suspect there are no shortage of new skills we will need to learn in the future to make sense of our data.

    Mobile technology, whether with cell phones or transportation (planes, trains, and automobiles), will become more prevalent in our lives in the next decade. I suspect this will mean many more opportunities for data professionals. Especially as I’m sure there will be new regulations and requirements that will keep software developers and database professionals busy modifying applications as legislation tries to catch up with the creativity of technologists.

    Steve Jones


    The Voice of the DBA Podcasts

    We publish three versions of the podcast each day for you to enjoy.