Tag: administration

  • Password for SQL Server Service Accounts

    I wrote recently about my philosophy for service accounts, and wanted to add a few more thoughts.

    Security is important for our database servers. One of the loopholes that everyone should be aware of is that the service running SQL Server has complete control over the service and potentially if this account were compromised, the security of our installation would be at risk.

    In this post I wanted to address two things related to service account passwords. The mechanics of building and working with these passwords and the ongoing maintenance in terms of changing the passwords.

    Creating Passwords

    One of the tools I recommend for anyone administering computer systems, including my parents on their personal computers, is a password manager. There should be a way for you to create and store complex passwords that are not easily guessed. I use Password Safe, but 1Password, KeyPass, and others are just as good.

    Typically I’ve used these to store the administrative passwords for various systems for all DBAs, sysops, etc. to use. However I haven’t used these for service accounts.

    Why not?

    Mostly because I don’t think any of us should be logging in as services. Apart from initial setup and testing, we shouldn’t use service accounts for anything.

    I always recommend long, complex, random passwords for services. The password should be created and written down long enough for someone to enter it twice in the areas reserved for credentials, and then the paper should be destroyed.

    I write these down because I want extremely long (20+), random strings that aren’t memorable and are really a one-time use string. Used just long enough to enter into the Services applet or as a credential in a PoSh (or other) script.

    If you use groups for your account rights, and you should even for service accounts (SQL Server makes this easy), you can always use another account to test access. Grant it the same permissions and groups, and perform your tests.

    Changing Passwords

    I don’t worry about changing service account passwords. Yes, I know this isn’t recommended, but services rarely change or are used to log on, we can limit the access of an account to a particular machine, and since the password isn’t stored, it’s not very vulnerable to cracking.

    If you are worried, then create a new, long, random string for the particular service(s) that are suspected to be vulnerable.

    I don’t allow expiration of service account passwords, though in a few organizations that have required yearly service account password changes, we’ve scheduled the changes for slow periods, not waiting until the expiration occurred. I can almost guarantee that accounts will expire during a critical time when machines should not go down.

    One caution. I know that changing passwords to long, complex strings is hard, and that there’s a temptation to set services to the same password or use some pattern to build passwords.

    Don’t.

    Patterns are poor security, and coupling services together with the same password (or account) is not worth the risk of issues if one system requires a change or the password is disclosed.
    banner_468x60_2015_speaking

  • My SQL Server Service Account Philosophy

    Recently someone sent me a question about service accounts. They weren’t sure how they should go about setting accounts up for various instances and services in their environments. Specifically they asked me about having domain accounts, or accounts separate for services.

    Note that I’ve managed SQL Server for years this way in environments up to hundreds of instances. I haven’t managed thousands, so there might be issues with this philosophy at scale.

    Here’s how I view service accounts. In a short list, I try to manage things like this:

    • Domain accounts for the SQL database engine and SQL Agent
    • Separate accounts for all instances and all Agent services
    • Long, complex, one-time passwords that aren’t stored.

    This has worked well for me, providing separation of services so that password changes or security issues on one instance don’t affect other instances.

    It’s also been scalable in that I rarely setup SQL Server instances. In most organizations I’ve worked in, we are adding a few instances a week at the most. The overhead to create two new accounts per instance (db engine and Agent) is minimal.

    Note that I would also have a separate domain account for SSAS or other items I install.

    With today’s rapid provisioning of machines through virtualized environments, I realize this isn’t necessarily a good hard and fast rule. If I expect an instance to be a production level instance and live for some period of time in the organization, I’d follow this philosophy.

    However if I am bringing online development and test instances that may not be kept around permanently, I think the local service accounts are fine. These will probably handle your needs and are worth scripting into your VM/instance creation process.

    I’ll add a few more thoughts on this across other posts, but there’s my idea in a nutshell.

  • No Defaults – T-SQL Tuesday #68

    tsqltuesday

    It’s the second Tuesday of the month, and time for T-SQL Tuesday. This month’s invitation is from Andy Yun, where he asks you to Just Say No to Defaults.

    This is the monthly blog party started by Adam Machanic, and it’s the chance for you to write on a particular topic every month. The hosts rotate, so you have to watch the #tsql2sday hashtag for the topic. Posts for the month need to go live during the day according to UTC time.

    I also keep a list of topics on the blog here, and you should feel free to write about any past topics and post something on your blog. It’s great practice, and a good way to get started as a #SQLNewBlogger.

    Default Changes

    There are all sorts of defaults in SQL Server. The setup program presents you with a number of choices, but in most cases a default exists for setting because SQL Server needs something.

    I used to have a setup script that I would run for every new install. In a few jobs, back when we used to have physical servers, a hardware person or sysadmin would install Windows and SQL Server onto a new computer and then send me the name for customization. My script, which was really a series of SQLCMD calls in a batch file that in turn called various other scripts, was designed to add an administrative database, create some jobs to track the system, setup backups, and more.

    The process really did part of what Policy Based Management can do, but was simpler and tailored to ensure that all of our SQL Servers worked in a similar manner. We could override settings, but this quick script gave us a starting point that all DBAs understood. We even ran this on development machines for instances we didn’t manage as it allowed us to troubleshoot other issues, it only took a few minutes, and it removed some of the management headaches from the developers’ minds.

    However, there is one thing I’ve almost always changed on my instances. I try to do it during setup, but at times I need to do it later. That setting is the default location for files. I do this as I want to usually have data files, log files, and backup files separate from each other.

    Even if I don’t have different drives, but setting up separate locations here now, I can easily move the files later and make one change here for the defaults and I know I’ll have things separate.

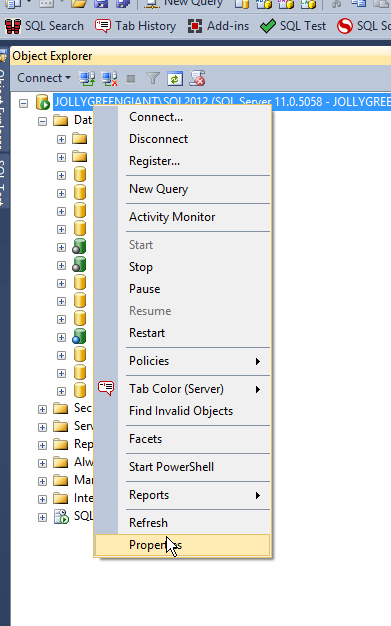
    I’m not running a new install this week, but I’ll show you how to change it on an instance that’s installed. First, right click the instance in Object Explorer and click Properties.

    2015-07-06 14_17_48-SQLQuery2.sql - not connected_ - Microsoft SQL Server Management Studio

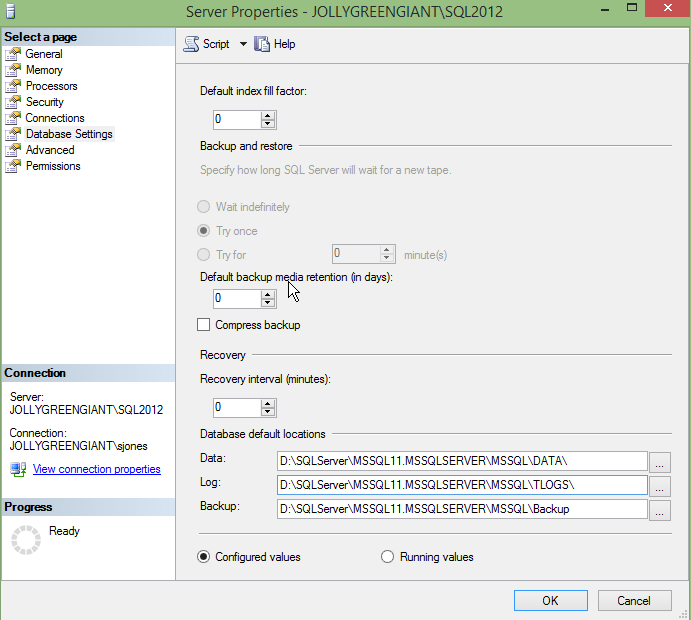
    Next, go to the Database Settings section.

    2015-07-06 14_24_07-Server Properties - JOLLYGREENGIANT_SQL2012

    At the bottom here you see locations for data, log, and backup. In this case, on my laptop, I only have two drives, so I can’t achieve great separation.

    However in any production system, I’d have the data and logs separated to different physical drives, or at least different LUNs. Backups might go with logs, but they’d ideally be separated to another location.

  • Does It Count?

    This editorial was originally published on Jan 28, 2011. It is being re-run as Steve is out of town.

    I wrote a blog recently about downtime and SLAs, and the need to have not only downtime SLAs, but also a data loss SLA. Thanks to Paul Randal (blog | @PaulRandal) for clueing me in to the need for having both. In the comments someone mentioned that scheduled downtime ought not be counted against your uptime measurements. That’s a debate I’ve had in the past with employers, and I thought it would be a good Friday poll:

    Should scheduled maintenance be counted against your downtime SLA?

    There’s an argument that says since the outage is scheduled, and people are informed, that this shouldn’t really count against your work in keeping servers running. The flip side is that when the database instance is down, it’s not useable, and of limited use to the business.

    I know that companies that calculate the usage of their vehicles, and maintenance counts against usage time. While it’s necessary, the idea is that mechanics should be looking to minimize it, and perhaps ensure that extra checks are done when the vehicle is being worked on to help prevent future issues. A similar argument could be made for database servers.

    Do you feel that scheduled maintenance is downtime? Is it calculated that way at your employer? Let us know this Friday.

    Steve Jones