Tag: security

  • Creating a Service Master Key in SQL Server

    The basis for all the encryption in SQL Server is the Service Master Key, which is the top of the encryption hierarchy. You can see the image below from Books Online of how this is setup.

    The service master key is automatically created when you create a key that needs it, usually a database master key. So there is no CREATE SERVICE MASTER KEY command.

    This key is encrypted and protected by the Windows DPAPI and the linked to the SQL Server service account. Since it secures all other keys in the encryption hierarchy, if you regenerate it, or restore it, all other keys it protects must be decrypted and re-encrypted. That can be a resource intensive operation, so don’t do that lightly.

    You can regenerate a service master key, and you do that with the ALTER SERVICE MASTER KEY command like this:

    ALTER SERVICE MASTER KEY REGENERATE

    That’s it. If it works, no errors, no results. If an error occurs, you’d need to deal with it. However this isn’t something you should run often, and if you encounter errors while doing this, I’d suggest you immediately stop, backup all databases and master keys, and then work through the issues.

    In another post, I’ll talk a little about the alterations you can make to the Service Master Key and how to back it up or restore it.
  • Be careful with your smartphone

    I love my iOS device and find it very handy.

    More and more tech professionals I know are carrying smartphones. There seems to be a split among technical people between iOS, Android, or WP7 platforms, but it seems that all the mobile OSes are extremely handy for system administrators. I know that I appreciate the ability to connect to email and other people when I’m away from my desk. If I were a production DBA, the ability to potentially fix something remotely, without the need to go to the office or back home, would be extremely valuable.

    However, carrying around a smartphone isn’t without a risk. The features and capabilities of the various mobile operating systems are a double edged sword. The power of the smartphone can easily be used for attacks against your network. This piece talks about hackers targeting the mobile platforms as another attack vector. That’s scary, especially as most of these mobile OSes were not designed to be secure.

    One of the very attractive parts of the Android platform is it’s openness. Anyone can build an app and sell it in the Android Marketplace. However that openness also means that the marketplace is a target for malware. While you might not like the Apple review process, it does offer some security. I’m not sure how the Windows Phone 7 platform is affected, but I would hope there is some security review. I also hope third party stores, like the Amazon Android store, will do some kind of security review to prevent malware.

    Ultimately if you are a privileged user on a corporate network, and you connect from your smartphone, you need to be extra careful. Set a password on your phone, don’t save passwords to trusted systems in your mobile browser, and be especially careful about scanning your system regularly.

    Steve Jones


    The Voice of the DBA Podcasts

  • How to change the SQL Server service account

    It’s easy. First you click here:

    serviceaccount1

    Then you find the SQL Server 2008 or 2008 R2 program group

    serviceaccount2

    Open those and then pick the SQL Server Configuration Manager.

    serviceaccount3

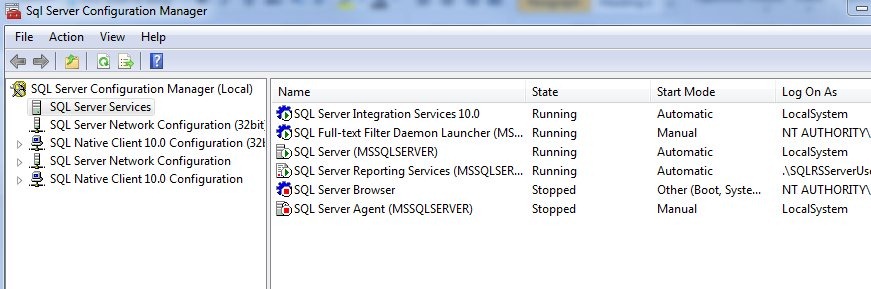
    You might get a UAC message asking if you want to make changes to the system, and say yes. This application can change service accounts, which is a sysadmin function. The screen basically looks like this:

    serviceaccount4

    If you right click the SQL Server entry, the database engine, you can select the properties, and you’ll get this screen:

    serviceaccount6

    On this screen, you can change the service account, and this is where you should change it. There are the three built in accounts in the top drop down (Local System, Local Service, and Network Service). I don’t recommend these. Instead, I recommend you create a new Active Directory Domain account (or local user account), assign it no rights, and then use the lower radio button to select the account.

    serviceaccount7

    Note that you do can search for it, and also you need to enter the user account. The password, while conforming to your domain policy, shouldn’t be one you use elsewhere. Make it a long, impossible to guess combination of stuff. You don’t need to recover this or log on as the user after you’ve assigned it to SQL Server. If you need to recover the password, just change it.

    A couple quick notes, on the Service Tab you can set the startup mode (Manual, automatic) for the database engine.

    serviceaccount8

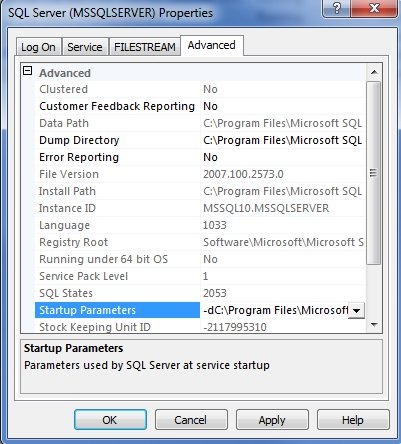
    You can also change startup parameters here, on the Advanced tab.

    serviceaccount9

    That’s it, it’s easy, and it’s how you should change the service account for SQL Server.

  • Encryption Works

    If you have better encryption than this, it will work.

    I don’t know that the government hires the best people or they have the best tools to work with, but they have some expertise. There’s a short note from Bruce Schneier that full disk encryption (FDE) does appear to by preventing unauthorized access to computer systems by police in many cases.

    If you read the comments, there are all sorts of flaws and potential holes with encryption, which are valid arguments. However that doesn’t mean that you shouldn’t implement any encryption on your removable or portable drives, especially those in laptops. Those devices are like the locks on your home or car. They can be defeated by determined professionals, but all too often the casual criminal doesn’t bother if they are in place.

    Keep in mind many laptops are lost, stolen, or sold without wiping the drives. Most people that received the drive wouldn’t bother to try and decrypt it unless they were sure it had something valuable on the drive. Since it’s no guarantee that a laptop grabbed at Starbucks or from a car has valuable data, most likely the target is the hardware, not the disk contents.

    I think disk encryption is a good layer of defense in your security strategy and worth implementing. My laptops are encrypted, mostly because it’s an easy security mechanism, and I’m not always sure if something I have on there is sensitive enough to worry about. My recommendation is that you implement FDE if you can.

    You should also make sure you are backing up your data. Losing the laptop might not result in the release of sensitive data, but losing the data itself could be a major problem.

    Steve Jones


    The Voice of the DBA Podcasts