Tag: security

  • Changing the Owner Removes Permissions: #SQLNewBlogger

    This is actually inspired by an article SQL Server Central, which taught me something new. I decided to verify what was in the article and do some research. The summary

    tl;dr if you change the schema owner, all permissions are dropped.

    Another post for me that is simple and hopefully serves as an example for people trying to get blogging as #SQLNewBloggers.

    The Scenario

    We start by creating three logins and their corresponding database users. Think of them as three colleagues with different roles:

    • User1 — will own the schema
    • User2 — will be granted access to a table
    • User3 — will eventually take over schema ownership

    Imagine there are a lot of User2 variants, as different logins are granted access to this table. To me, this is a problem, and I would use a role if I managed the system.

    CREATE LOGIN User1 WITH PASSWORD = 'Demo12#1'
    CREATE USER User1 FOR LOGIN User1
    GO
    CREATE LOGIN User2 WITH PASSWORD = 'Demo12#2'
    CREATE USER User2 FOR LOGIN User2
    GO
    CREATE LOGIN User3 WITH PASSWORD = 'Demo12#3'
    CREATE USER User3 FOR LOGIN User3
    GO

    Next, we create a schema explicitly authorised to User1, then add a table to it and populate it with some sample data.

    CREATE SCHEMA MySchema AUTHORIZATION User1
    GO
    CREATE TABLE MySchema.MyTable (myid INT)
    GO
    INSERT MySchema.MyTable (myid)
    VALUES (1), (2), (3)
    GO
    SELECT * FROM MySchema.MyTable
    GO

    At this point, User1 owns MySchema. Any objects inside it — like MyTable — fall under that ownership.

    Now we grant User2 SELECT permission on the table. This is straightforward, explicit, and intentional. I’ll perform an explicit grant of permissions here.

    GRANT SELECT ON MySchema.MyTable TO User2
    GO

    We can verify it works by impersonating User2 and running the query:

    SETUSER 'User2'
    GO
    SELECT * FROM MySchema.MyTable
    GO
    SETUSER
    GO

    The query succeeds and returns all three rows. So far, everything is working as expected, as we see below..

    2026-06_0119

    Now, the tricky part I didn’t know.

    Here’s where things get interesting. A database administrator decides to transfer ownership of MySchema from User1 to User3:

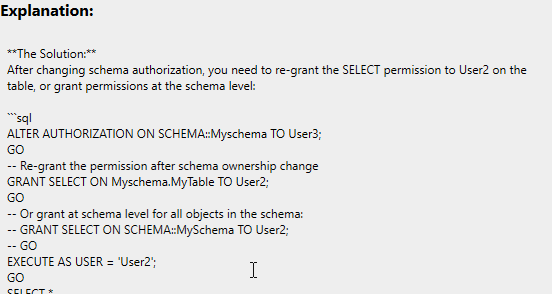
    ALTER AUTHORIZATION ON SCHEMA::MySchema TO User3;
    GO

    This might seem like a routine administrative change — just updating who “owns” the schema. No permissions were explicitly revoked. No error is raised. But something has quietly changed.

    If I now run the code above, I can’t access the table as User2.

    2026-06_0120

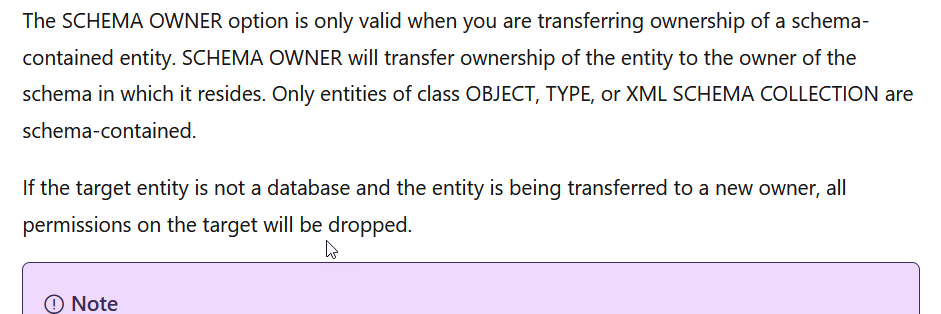
    I’ve lost access. If I check the ALTER AUTHORIZATION docs, I see this, with the last sentence being the important one. Permissions are dropped.
    2026-06_0122

    Something to know, and glad that Prompt AI knows this:
    2026-06_0121

    Summary

    If you change the owner (authorization) on an object, and it’s not a database, permissions are dropped. This should be a warning at the very least, though to be fair, I’ve never changed schema ownership. It could happen, but in general, I try to keep dbo as the owner of all schemas.

    In any case, something good to know.

    SQL New Blogger

    I took some code from an article I read (edited, really) and then used it to setup a scenario to test the concept. I likely will never forget this, and if I an AI suggests this, or can’t figure out what went wrong, I’ll have some idea myself to verify or validate a fix.

    This post took about 20 minutes, including running the code a few times to test things, but it was a good exercise to show what I know, how I can use AI, and how I can spot issues.

    You could use something like this as a learning exercise and to showcase your skills, even in the age of AI.

  • The New Wave of Security Threats

    We’ve had quite a few GDR patches for SQL Server released this year. If I glance at the Build Lists I maintain, I see Sept 2025, Nov 2025, Jan 2026, and Mar 2026 GDR patches. That seems rather frequent as the history of builds for recent versions has often seen them without any GDR, out-of-band patches. Just CU after CU every other month.

    That pattern of rare security updates might be changing for lots of software, not just SQL Server. There was an article recently that noted AI tools might start exposing lots of bugs, including security holes, in software that has been around for years. Someone recently used AI found bugs in both PostgreSQL and MariaDB that have been around for years. They are patched, so if you run those platforms, make sure you patch things. The information is out there and someone is looking to take advantage of it.

    Anthropic built a new model, Mythos, which has not been released publicly. It’s been given to a few customers who have used it in testing, and it seems that it might be more capable than expected at finding bugs. Hopefully, we will find out how good it is soon and lots of companies can use it to examine software. It’s certainly a danger as hackers and criminals might use it, but I believe that (responsible) information disclosure is better for everyone.

    This is also a good reminder that you need to patch your systems. I certainly get wary about updating on day 1, but I do try to patch without too much of a lag. There are no shortage of zero-day attacks, but I also weigh the risk of instability from patches of questionable quality. Many vendors do a great job of patches and upgrades most of the time, but “many” and “most” aren’t “all”, so I prefer to let others test early. Someone has to apply the patches on day 1, but I don’t want it to be me.

    Security is getting harder, it’s getting more burdensome, and it’s becoming more important. At the same time, lots of people are building better security with new tools, including AI. Just make sure you apply those patches to take advantage of their work.

    Steve Jones

  • A Cloud Dependency Failure from Amazon

    I went to sleep while reading a Kindle book on my phone. I know because my hand dropped and the phone knocked me in the forehead. I set it on the nightstand and went to sleep again.

    I woke up and was planning on reading for a few minutes before starting my Monday. When I opened the Kindle app, it asked me to log in. When I did, Amazon said my account was locked and I needed to check an email. I did, and found one from Amazon.co.uk questioning a purchase I made and asking for me to very an order number and the last 2 digits of a card to charge.

    I wasn’t sure what to do, but since my wife was complaining about her Audible account, I knew I needed to do something.

    I didn’t like the email for multiple security reasons, including not giving me a way to verify the email online. Checking Amazon’s help page said I should have a link in the email to a form. Even when I called the Amazon help line, they said I should have a link when I logged in to do so. I didn’t on either the .com or .co.uk sites, but Amazon Customer Service eventually unlocked my account.

    I wrote about Dependencies in today’s editorial, inspired by this story and the Reddit story linked in there about losing access to Claude. That’s scrary, especially in this new automated world where AI agents might be examining activity and undertake this type of action to prevent other issues. It’s an overreaching type of judgment that starts to expose the dangers of a highly interconnected world.

    I get Amazon might want to ensure my purchase was legitimate and perhaps prevent future orders, but also locking my content away (books, movies, audio, etc.) because of a shopping issue seems extreme.

    It’s certainly my issue, and I’m not sure how I untangle things for the future, but it does make me think about limiting dependencies a bit more in the future. Or at least understanding the dangers of too much on one service.

    Whether that’s the books I read or the services my company gets from any one vendor.

  • Local Agents

    Recently I saw an interesting article, saying that someone could build a general purpose coding agent in 131 lines of Python code. That’s a neat idea, though I’m not sure that this is better than just using Claude Code, especially as the agent still uses the online version of  the Claude model from Anthropic to generate code or perform other tasks. There’s a video in the article showing how this code can be used to perform some quick tasks on a computer.

    However, the code isn’t specific to Anthropic. It can be used with any LLM, and I started doing just that, with a copy of the code from the article, but modified to use a local AI LLM running under Ollama. You can see my repo and feel free to download and play with it. It’s expecting a local LLM on 11434.

    I’m a big fan of local agents for a variety of reasons, but mostly because I know humans tend to do dumb things. Especially with new technology, and maybe even more especially in development areas.

    That includes me.

    I’ll take shortcuts. I’ll give an agent sysadmin on a dev database to try things. I want to be able to experiment, learn, and see what works. I want to learn how to use tools and fail using them. That’s how I get better. That’s how I get better in sports, in music, and in technology.

    And that’s not a project I can take time to work on. I don’t get to dedicate time to just learn and then go back to work. Work never ends. It’s a grinding, constant, continuous treadmill of things I need to deliver to others. I have to learn to experiment around those deliverables when I can find spare moments.

    With AI, that means we’ll do things that get InfoSec teams to cringe. I get the concerns over data transiting networks and going to who-knows-where to be used who-knows-how-by-others. I appreciate business subscriptions that guarantee that data won’t be used, but I also want extra safeguards at times. That means local models. Not necessarily on my laptop, but in my data center.

    Plus, that way I (or my org) can control the costs and manage expectations.

    I hope local models and local agents catch on, I hope more vendors support them and more organizations are willing to run them. Even in something like AWS Bedrock or Azure Open AI or Vertex AI. Then I can rent the latest and greatest hardware, but have more control over how my organization uses it.

    Steve Jones

    Listen to the podcast at Libsyn, Spotify, or iTunes.

    Note, podcasts are only available for a limited time online.