Tag: security

  • Better Protection from Hardware

    Microsoft is working on ways to protect your system at an even lower level than the bootloader. Many modern computers have UEFI protection, which allows for security in the boot process, and prevents untrusted code from running. This is intended to ensure that some other boot process cannot run and then invoke your Windows bootloader

    This doesn’t protect from firmware issues, but Microsoft may have a solution. Working with hardware companies (Intel, AMD), they have a System Guard Secure Launch that provides a way to secure your OS. There’s a light explanation at Ars Technica of what this means for you. Essentially, this allows the OS to reset the CPU and ensure untrusted firmware code isn’t running

    I won’t pretend to know how this works in depth, or what additional levels of security this provides, but I do recognize the problem being worked on here. I also think that criminals (and rogue nation state actors) are making deeper and more complex attacks on systems. We know that compromised code can be a major problem for our servers, and we need better mechanisms to ensure we can trust the platform on which we run our database servers

    Just recently there was an alert about a backdoor in SQL Server. This was noted as being in SQL Server 2012 and 2014. At first I was surprised this didn’t get more play, then I realized this was an issue with the Windows OS being compromised and then a patch installed on the SQL Server service to allow attackers to log into the database server. Disconcerting, but if someone gains control of the Windows OS, I’d expect they can get into SQL Server.

    Security is a problem with database servers, and the number and variety of attacks continues to grow. It pays to be diligent, and certainly, use whatever tools are available. Strong passwords, access controls and low privileged accounts, UEFI, SGSL, set up every security feature you can. After all, data is your organization’s most important asset.

    Steve Jones

    Listen to the podcast at Libsyn, Stitcher or iTunes.
  • Data for Defense

    It’s a dangerous world out there. Many of us hear about data breaches on a regular basis, and we often blame poor security at various organizations. Certainly there are a lot of silly mistakes made, whether in configuration or the mishandling of data in insecure environments. Security is a tough business, however, and most organizations don’t have the budget to combat all the threats they face, at least not as effectively as a larger organization could.

    I have more sympathy for organizations after reading about the work of some Microsoft security teams that go up against the world’s best hackers on a daily basis. To truly understand the vulnerabilities in software, someone must also understand how to attack it. Those of us that only have a defensive mindset are inherently limited in how we design protective measures.

    There is a group, the Microsoft Threat Intelligence Center (MSTIC), that looks for and tracks hackers around the world, trying to understand how they attack organizations. This is a group of multiple teams looking at nation state attacks, as well as complex software tricks, using the tremendous amount of data they gather from telemetry to analyze the different techniques and vectors used to exploit holes in our systems. They notify customers, letting them know when a customer need to be prepared to defend themselves.

    This is a fascinating read, and one that makes me think that most of our organizations are going to be at cyberwar for the foreseeable future. Already we know that any system on the Internet is likely to be probed and attacked if it has vulnerabilities. Most of us are careful about what we expose, but we also know the weakest link in our organization could cause us issues.

    We do the best we can, but often we do depend on other organizations, like Microsoft, to actively be identifying and helping us understand what to patch or change to protect ourselves. I assume Google and Apple have similar groups, notifying their customers of potential threats. These large vendors are likely the best positioned to help, given all the data they collect about their platforms. Certainly I worry about data privacy with these vendors, but I do think that their massive troves of data on how their software works can also benefit all of us.

    Steve Jones

    Listen to the podcast at Libsyn, Stitcher or iTunes.
  • The Ransomware Hero

    One of the common attacks against many organizations today is ransomware. I’m constantly surprised when I see friends and they tell me they’ve been attacked, but the incident never made the news. I think many people would be upset with businesses if they knew the extent of attacks, but I also think that this would force more organizations to implement better security if shareholders and customers were aware of the incidents. This might even get employees and others to be more careful about the things they click and do, though that might be wishful thinking.

    In Illinois, in the US, there is a guy that is fighting ransomware and helping out both organizations and individuals. For free, which is much better than paying the fee, something plenty of organizations have done. Michael Gillespie runs ID Ransomware, a site that helps you determine what type of attack you’ve had. It can also possibly give you or generate a key that will allow you to decrypt your files.

    This man does this in his spare time, while working as a computer support person. It’s an amazing story, and one that is a little sad. Here is this man that doesn’t want to charge, and wants to help, but has struggled financially while doing so. Things have gotten better, and more people are supporting his efforts, including Emsisoft, who has hired him part time.

    If you get struck, it might be worth a visit to ID Ransomware and see if you can get some help. If you do, convince your boss to donate some payment to support Michael’s efforts. It’s a good cause, and certainly cheaper than paying a fee or losing lots of work while you try to sort out the problems.

    Steve Jones

    Listen to the podcast at Libsyn, Stitcher or iTunes.
  • Setting Certificate Backup Permissions for an Instance–#SQLNewBlogger

    Another post for me that is simple and hopefully serves as an example for people trying to get blogging as #SQLNewBloggers.

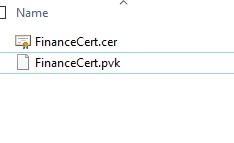
    Recently I was testing some security change, and I made a backup of my certificate from one instance. I did this on a share that I’ll use to move the files to another instance. In this case, I had these files in the folder.

    2019-08-23 14_31_13-SQL

    The problem is that by default, SQL Server locks down permissions, as it should. That means that the other instance couldn’t access the files, as its service account didn’t have permissions.

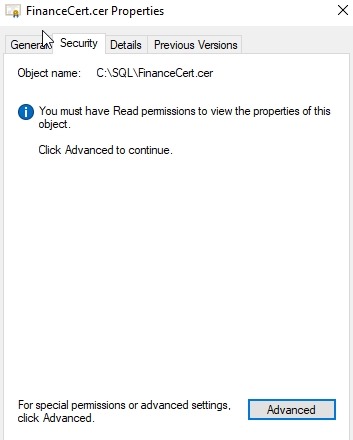
    I fixed this by opening the security tab for the file. I had to do this for each, but I’ll show one here.

    2019-08-23 14_31_22-FinanceCert.cer Properties

    I clicked “Advanced” to get a more detailed view of permissions.

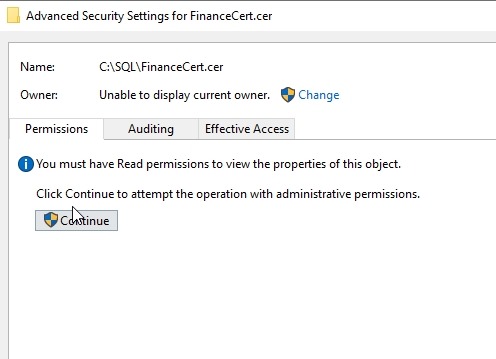
    2019-08-23 14_31_28-Advanced Security Settings for FinanceCert.cer

    Again, I really need to approve this view of the security settings. Once I acknowledge the UAC dialog, I can see this:

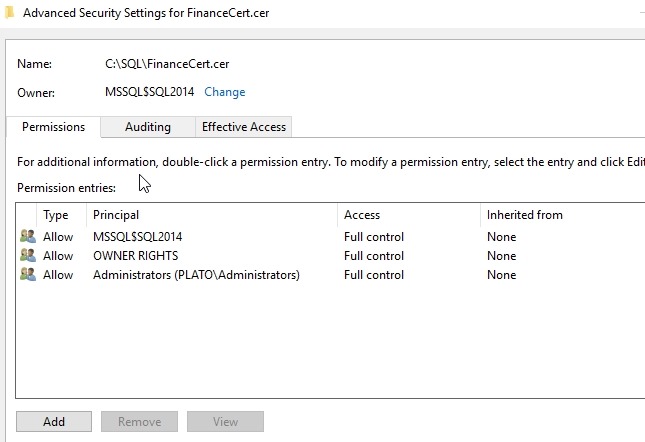
    2019-08-23 14_31_38-Advanced Security Settings for FinanceCert.cer

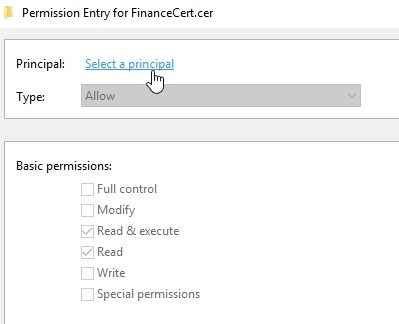
    What I needed to do here was add permissions for another service account. Clicking Add lets me select a principal.

    2019-08-23 14_31_46-Permission Entry for FinanceCert.cer

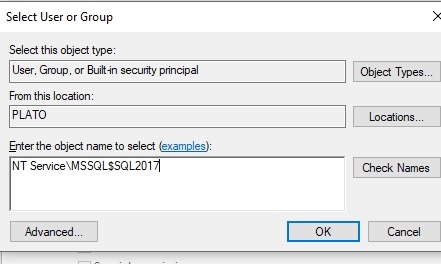
    For a local account, I need to give the “NT Service” prefix to my account, despite this not being shown as part of the service account settings.

    2019-08-23 14_31_57-Permission Entry for FinanceCert.cer

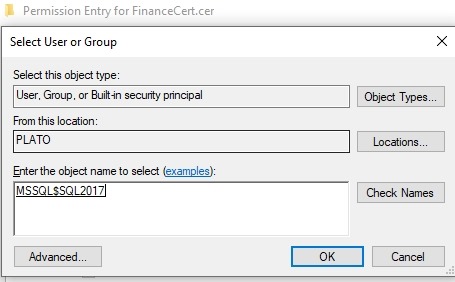
    When you click Check Names, this will shorten. If you enter this short version, it won’t work.

    2019-08-23 14_32_01-Permission Entry for FinanceCert.cer

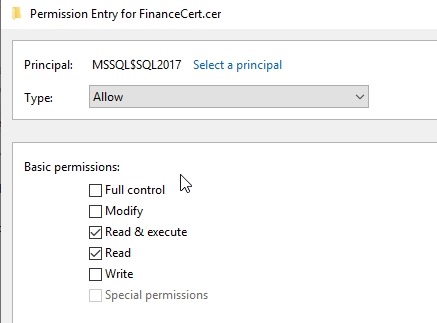
    In my case, this account really just needs Read permissions.

    2019-08-23 14_32_05-Permission Entry for FinanceCert.cer

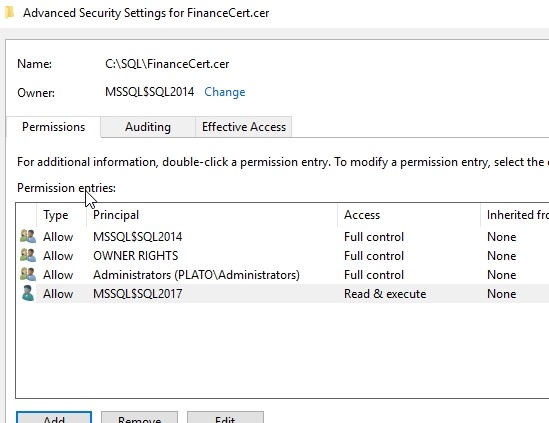
    Click OK, and I see it listed.

    2019-08-23 14_32_10-Advanced Security Settings for FinanceCert.cer

    That’s it. Now my SQL2017 instance can access the backup and create the certificate.

    SQLNewBlogger

    This is something I’d expect most people working with SQL Server on Windows would be easily able to do, but showing some knowledge here gives confidence in your abilities.

    This took longer to get screenshots than to write. You could easily do something similar.