Tag: security

  • The Security Weak Link

    I saw this cartoon, which I think is great: Data Security. It’s from John Klossner, and it perfectly shows that humans are, and probably always will be, a weak link.

    I look at this in two ways. First, we need to account for and accept that our users will make mistakes, so we need to have security in place, but also monitoring that detects issues. The second item is that this could be a privileged user, so the less we need privileged users to actually access and do things, as in manually changes or deployments, and the more we require them to “submit” changes that are audited, the better off we are.

  • Deleting a User that Owns a Schema

    This was an interesting question I saw posted recently. Through SQL Server 2000, trying to delete a user that owned objects was a pain. We had to actually rebuild all the objects, which was problematic. With SQL Server 2005 and later, we got schemas actually added as separate entities, so that solves some of the issue.

    To allow a user to be removed from a database when they own a schema, we need to move the ownership, or authorization of the schema to a new user.

    Here’s a short repro of what to do.

    Let’s say that I have a user in my database called SallyDev. This user is a DDL_admin and can create objects. I’ll add Sally to my database with this script:

    CREATE LOGIN SallyDev WITH PASSWORD ='SomethingStrong'
    GO
    CREATE USER SallyDev FOR LOGIN SallyDev
    GO
    ALTER ROLE db_ddladmin ADD MEMBER SallyDev
    GO

    As such. SallyDev has run this script:

    CREATE SCHEMA SallyDev
    GO
    CREATE TABLE SallyDev.Class
    ( ClassKey INT IDENTITY(1,1)
    , ClassName VARCHAR(100)
    , Active BIT
    )

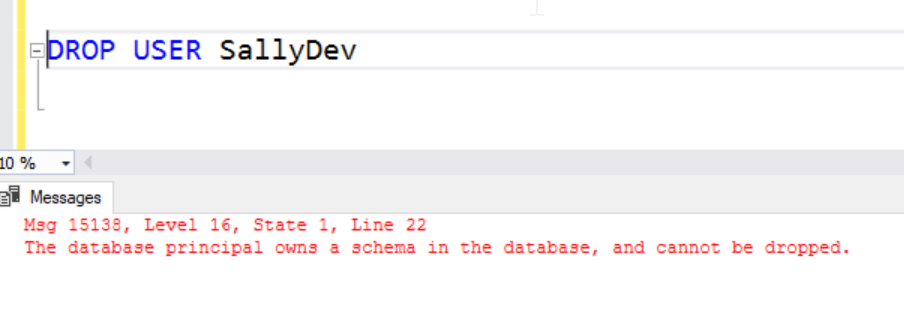
    Now, SallyDev has left the team and we need to remove her user and login. When we try to remove the user, we get this error:

    2018-09-15 01_02_05-SQLQuery1.sql - dkrSpectre_sql2017.sandbox (DKRSPECTRE_way0u (68))_ - Microsoft

    In SQL 2000, Sally would have owned the table and we would have gotten a different message. Now, Sally owns the schema, but the schema now owns the table.

    To fix this, we need a new owner for the schema. We can use any user with the ALTER AUTHRORIZATION command like this:

    ALTER AUTHORIZATION ON SCHEMA::SallyDev TO JoeDev

    I don’t recommend another user as we are just deferring the same problem. Instead, I’d move the schema to dbo.

    ALTER AUTHORIZATION ON SCHEMA::SallyDev TO dbo

    Once this is complete, we can drop the SallyDev user.

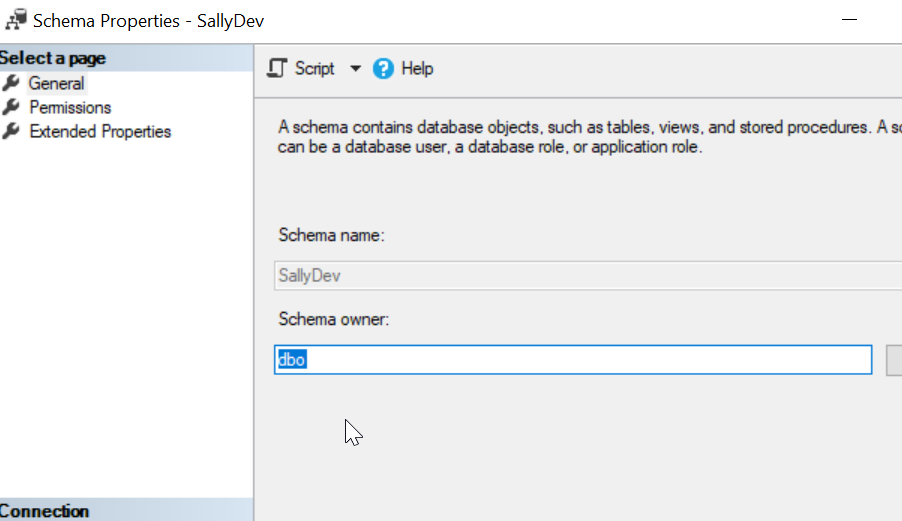
    We can also verify the schema has moved to a new user.
    2018-09-15 01_06_37-Schema Properties - SallyDev

  • Protecting Our Stream of Data

    Protecting the data our companies collect is important. Many of us go to great lengths to secure our databases, firewall connections, limit access, and more. However, we can’t secure the data before it gets to us, and that can be a problem. I ran across a link on Bruce Schneier’s blog that shows a criminal placing a skimmer on a credit card scanner in a convenience store. The original video is gone, but there are plenty more.

    In general, the loss of data from the application (and physical hardware in this case), isn’t really a database issue. After all, the data is essentially split into two streams, with some going to the legitimate database and other processes while another stream goes to the skimmer. If this happens, and the skimmer isn’t discovered, however, it’s entirely possible that any data loss might be blamed on the database or IT infrastructure.

    If someone suspected you were hacked because of data being lost, could you prove you weren’t hacked? Or that the data didn’t come from your database? This is impossible, since you can’t prove a negative, but would you have any evidence that could be used to bolster your claims? Is there auditing or other tracking of activity? Does your organization keep any logs that would show a lack of activity and are protected against tampering? Ideally you would find the source that lost the data, but if you can’t, it can be difficult to prove that the losses didn’t come from your systems.

    For most of us, we might not have much in the way that would show our systems have only had legitimate access. Instead we’d depend on the limited SQL Server logging, as well as other infrastructure tracking, such as firewall activity logs. The strength of our presentation would likely determine whether security staff or management accepted our claims as valid.

    Point of Sale systems are different than the applications that most of us use, but certainly we have database security concerns that we should address. I would hope that SQL Server would bolster its capabilities in this area, providing a way to set up a tamper proof log easily that accepts writes of activity from a database in some structured text file that uses minimal resources. I’m not even sure what I’d want here that I can’t get from XE, but I do think having something more robust and standardized would be nice. If nothing else, a local SQL Server could stream XE events out to a file target in a remote location that only supports writing. This wouldn’t necessarily prove anything if the connection were disrupted, but it would ensure that a business was aware of the breakdown between the instance and audit log.

    I know the ways in which people attempt to access and steal data will continue to evolve and become more complex and creative. We can’t protect against many of them from the database side, but I’d like to think that we could protect the data we have. We should ensure it is safe from theft, loss, or inappropriate access and prove we have done so.

    Steve Jones

    The Voice of the DBA Podcast

    Listen to the MP3 Audio ( 4.2MB) podcast or subscribe to the feed at iTunes and Libsyn.

  • The Weakest Link

    I noticed another data breach recently. This breach was from PageUp, a firm that helps companies find employees. This means that they have lots of information, potentially PII data, and some of it might be out there. Since they provide job sites for many other companies, you might have used them to apply for a job and not realized it. Certainly if you have used them, you might keep an eye out.

    The company notes that no personal information was lost, though encrypted usernames and passwords were disclosed. These were salted values encrypted wtih bcrypt, which is secure, but all encryption can be broken given time and effort. Some people see bcrypt as secure, but others disagree. However,  the strength of bcrypt depends on how the hashing was set up, and I wouldn’t depend on this to be foolproof. If you used a password to apply for a job that you use on other sites, change it.

    The bigger issue for me is near the end of the BBC piece. A bank notes that a third party supplier had a security issue, so that means they need to check their systems. To me this means one thing.

    Their security depends on the security of their business partners.

    Depending on the level of access and integration, this might mean that your security is compromised by a link much weaker than the weakest link in your internal environment. Or that your security depends on the weakest human link not only inside your organization, but also within your partners. Despite all the work you’ve done to increase the security of your systems, you might have other holes out there.

    It doesn’t appear this breach is as bad as originally thought, but the point is still valid. The more interconnected you are with partners, especially with shared access, the larger your attack surface area. I take away the need from this that I need to ensure a limited API and protected access with minimal privileges for internal systems that are connected to any other networks. Production level security is important not only to public facing systems, but also those that are semi-private with business partner access.

    Steve Jones

    The Voice of the DBA Podcast

    Listen to the MP3 Audio ( 3.0MB) podcast or subscribe to the feed at iTunes and Libsyn.