Author: way0utwest

  • Do You Need a Coach?

    Most of us reach a point in our careers where we think we can tackle most of the challenges we face ourselves. We may ask questions, we may need to read, study, practice, or more, but we tend to have the self confidence to go it alone, making our own decisions and giving ourselves feedback on how things work.

    However maybe there’s a better way. I read this piece about a surgeon that tried a coach and found it to be very helpful. To be fair, I’ve read Dr. Gawande’s book and enjoyed it: The Checklist Manifesto.

    It’s an interesting idea. We often pay teachers and coaches to help us with sports, with some areas of our lives, but most of us don’t bother. I wonder if there’s something that’s worth investing in here professionally.

    I think there is, and that’s probably the easy thing. Finding someone that you trust to be a coach, and you’d be willing to pay.

  • Anonymous Research

    Anonymity is important

    It’s no secret that anonomizing data doesn’t always work well. We have heard about this when Netflix released their data for people to build algorithms with. Some people were identified based on the data released being correlated with other data the people had entered on the Internet themselves. I know that there are dangers with sharing too much information on the Internet, but people are going to share and there will only be more services in the future for us to use that require data.

    I ran across a post recently from Microsoft researchers that showed similar issues with other anonymous data sets that contain IP information. A number of logs containing traffic from Bing and Hotmail were analyzed with the intention of identifying particular hosts. Even when the data was anonymized, it was possible to identify hosts with a high degree of accuracy.

    You might not think this is a big deal, but as more data is gathered by companies and used for secondary purposes, like analysis, it becomes more likely to be inappropriately released. Is a log on a server more secure, or a copies of multiple logs on analysts’ laptops? I’d think the former, or at least I’d hope the former. If that’s true, then we should really be anonymizing data on a regular basis once it leaves hardened server machines.

    That means we ought to have better algorithms for preventing any identifying information from being retrieved. I would hope that this is an area where research can help, and one that receives a lot of attention in the near future.

    Steve Jones


    The Voice of the DBA Podcasts

    We publish three versions of the podcast each day for you to enjoy.

  • Hardware Fun

    This has been a bit of a hardware week for me, which is strange. I used to love hardware, building my own computers, picking out the components, and making something work out of a pile of parts.

    Now I just want my tools to work.

    Our Windows Home Server died a few months ago. This is the third time I’d lost a boot drive in the WHS server, though to be fair I was reusing a few older drives in it. However when you lose the boot drive, not only do you need to reload WHS, but it can’t reload your content from the old drives. The drive extender technology is flawed, which is why it might be cut loose from the WHS 2011 product.

    I’ve delayed actually rebuilding things, but with my wife traveling one week, the kids occupied, I took it apart and connected the drives one at a time to check how things were working. They all connected and seemed to work, which was strange. Perhaps bad blocks?

    I reconnected the 160GB drive as the boot drive, since that was the smallest, added in two 1TB drives in a RAID 1 array, and a 1TB drive as a spare. I booted to WHS 2011, but it promptly failed. This is a Dell E521, an AMD x64 CPU, but it didn’t want to load. No problem, I was planning on virtualizing anyways.

    I booted to Windows 7 x64, and got through the initial install, but on boot, the 160GB drive failed. Aha! I removed that, replaced with a 1TB drive, and reloaded Windows 7.

    Only to find that there aren’t x64 drivers for a number of components for Win 7. Grrrr. This is why I don’t like to mess with hardware. I want stuff to just work.

    I fell back to Windows XP, x64 (since I want 64 bit guests) and got that installed. I had RAID drivers, but for some reason Windows setup doesn’t want to install them or load onto a RAID set. That feels like a waste of the purpose of hardware RAID, but whatever.  I got Windows loaded, patched, drivers installed, and added Virtual Box 4.

    Then the harder part. I created a guest on my R1 array, which too time for VirtualBox to format the drive. Once it was done, however, I booted up a guest, installing WHS 2007 on there and connecting to the network. I killed the host firewall, and bridged the network adapter. Not sure which one fixed things, but I don’t do anything on the host, and it’s firewalled from the outside world.

    Now I had two spare 2TB drives from the old system, where I copied off the pictures, video, and music to my desktop. A long transfer process in the background added them to the WHS server, and I have a home network again.

    It’s RAID protected, so I should be OK for now, but we’ll see what happens. I have an external enclosure with 2 2TB drives in it, but I don’t want to add them for now. At least until I need more space.
  • Encryption in Production

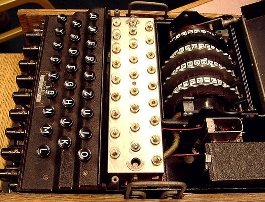
    WWII era encryption with the Enigma Machine

    The encryption capabilities of SQL Server have been growing in each new version. We have gone from password protected backups to Transparent Data Encryption (TDE), we have moved form PWDENCRYPT() to symmetric, asymmetric keys, and certificates. There are quite a few options available in the current SQL Server platform. However I don’t often see people writing or talking about their use of security.

    It might be the nature of sensitive data means keeping the use of encryption quiet, but that shouldn’t matter. If you are keeping your keys safe, the algorithms and deployments you use should not matter. This Friday I wanted to ask a question about your use of encryption in real world systems.

    If you have sensitive information (identity/financial/medical) data in a database, have you deployed encryption?

    I would like to know if you’ve actually implemented native or third party encryption and if so, in what percentage of the databases that have sensitive information is encrpytion deployed. Do you strip out data before you store it, perhaps only storing something like the last four digits of a credit card in plain text? How diligent do you think your employer is being with regards to encryption?

    If you work with encryption, are you confident that you can recover your systems in a disaster? That’s one question I’d want to be sure I could answer before I deployed any keys in my database.

    Steve Jones


    The Voice of the DBA Podcasts

    We publish three versions of the podcast each day for you to enjoy.