“This is the digital world IT must keep up with–one where Apple can view a $40,000 car as an accessory to the iPhone.” – From IT Is Too Darn Slow
The IT world definitely needs to learn to move quicker, and that means that we need to be more solid in our infrastructure. The basic tasks of setting up a server, getting it configured, building indexes, setting up maintenance, etc. need to be smoother and easier that more time, and more importantly, more resources can go to building new systems.
I’m in a fun mood today, so a few silly items for you.
The last few weeks, Paul Randal (blog | @PaulRandal) of SQLskills has been doing a quiz on Twitter some days. He’s asked some rather difficult questions on Twitter, and people have had fun following along. I decided to get in on the fun today with a few questions of my own as a “pre-test” to his quiz.
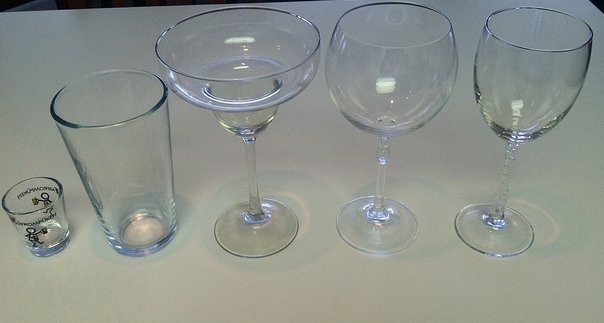
Question 1: Which of these glasses does Kimberly Tripp (blog | @KimberlyLTripp) prefer?
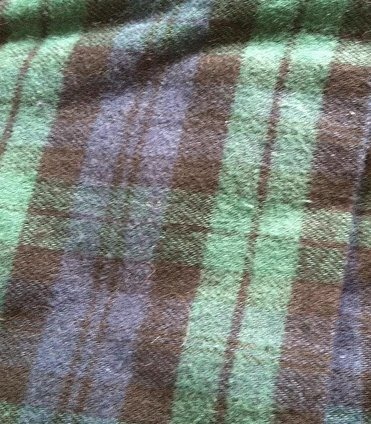
Question 2: What is this and is how does it relate to Paul Randal?
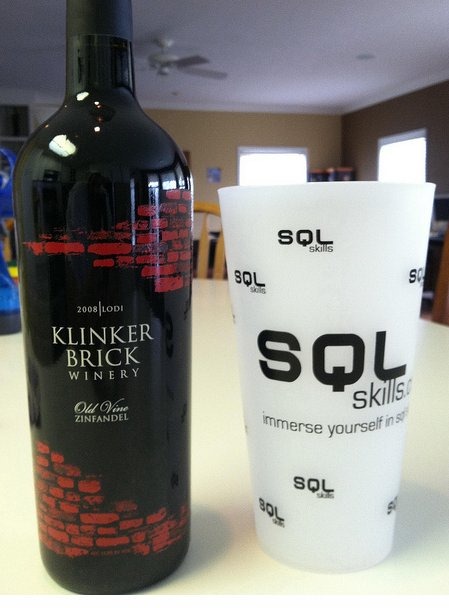
Question 3: Will it fit?
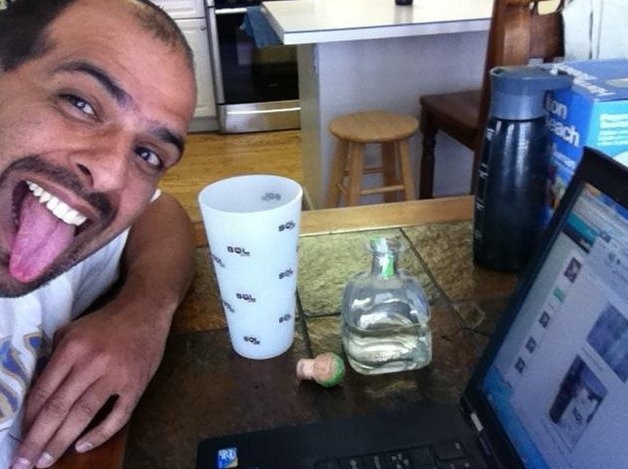
I’m having fun today, as you can see
In case you really want the answers:
A1: none of them; they’re all empty!
A2: It’s a kilt, which is a skirt for boys from Scotland. That’s where Paul was born.
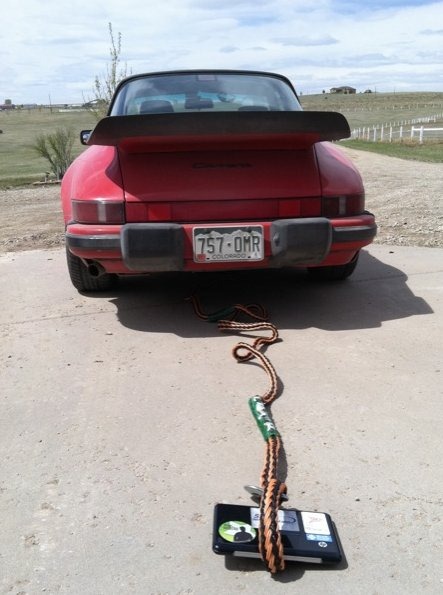
Simon Sabin had his own take on increasing laptop speed. He had some good ideas, but he inspired me to try to top his suggestions. Here’s what I came up with:
Suppose you found some malicious code on your system. Maybe it’s a login that didn’t below at the sysadmin level, or maybe a stored procedure that might disable a trigger, make a change, and re-enable the trigger. What do you do?
Suppose you stumbled upon a strange stored procedure in one of your databases. It wasn’t something you had coded, and it appeared to be altering permissions, maybe adding a login, or even querying sensitive data. What do you do?
The easy answer is to delete the procedure and go on about your day. Some of you might save a copy of the code, along with its permissions and make a note to check the system a week or two later and see if it needed to be there. However I’m not sure that is the best action to take.
If you are unaware of the origins of code, it can be detrimental to your system if you remove object. A legitimate stored procedure might cause application errors, which can result in some type of discipline. At the very least, managers might be upset with you for taking action without understanding the consequences.
I think a different approach might be better. Set up auditing or tracing, focusing on the code and documenting any actions. I would talk to security people and potentially initiate lower level tracing of the network to determine who is making use of this code. If it’s truly malicious code, it’s not necessarily your job to stop someone. Setting up the honeypot, documenting actions, and then allowing someone else to determine the final action might be the best way to deal with the situation.


 Voice of the DBA
