Tag: security

  • If only the US would follow …

    I saw this blog from Allan Hirt and I wish the US would adopt something strong like this. I’d actually like this to apply to all organizations, but certainly critical services need to be secure. If you follow the link, you’ll see that the UK government has warned their critical industries that if they do not have effective measures or safeguards against cyber attacks, they can be fined up to £17 million. That might not seem like a lot in some industries, but it should get some attention from executives. I’m not sure how many CxOs would keep their jobs if they incur that level of fine because they didn’t implement strong security measures.

    For now the requirements apply to the energy, transport, water, and health industries. These are deemed essential by the UK government. The UK government is expecting that along with data privacy changes to ensure GDPR compliance, that these industries need to implement better cyber security to prevent or limit attacks. This is part of guidance from the European Parliment, and it’s overdue. I just wish the US were as focused on pushing organizations to adopt security as a priority rather than an afterthought.

    Not that I want government to dictate specifics, but I do think that having a government authority that can stay up to date and evolve their view of what constitutes good security is a good idea. This could be similar to some sort of review and feedback situation that we have for auditing. Ultimately, I’d like there to be some group that can weigh in on good security practices for platforms and systems, probably with research and industry feedback, on what constitutes valid patch levels for systems and software. It would be valuable to know that your version of Windows or Debian or PHP or the database platform is insecure. Not that I want to create more of an upgrade treadmill, but using software means patching it.

    Perhaps this would drive more organizations to move to open source software, or perhaps more vendors to issue patches rapidly and lower their prices to compete. Maybe more importantly, it would press vendors of third party software to ensure they continue to develop security patches, perhaps even spelling out support lengths in contracts. The pressure to perform better would be useful in raising quality in the security area. One thing to note is that the intent isn’t to fine companies, but ask them to make valid risk assessments and take appropriate measures (with input from regulators).

    For now, I’d say that most UK organizations ought to start taking security more seriously. Making changes in platforms to prevent attacks and limit downtime will require some planning and foresight. You might not be in an industry affected today, but in two or three years that could change.

    Steve Jones

    The Voice of the DBA Podcast

    Listen to the MP3 Audio ( 3.9MB) podcast or subscribe to the feed at iTunes and Libsyn.
  • Is Security Catching On?

    This is a good sign, as a poll shows people want security over convenience, especially younger people. Surprisingly this is also true for older people, who likely don’t trust much of our new technology. This is the first time that a majority of poll respondents haven’t been happy to have some easy password acceptable or the convenience of linked accounts. More and more people are embracing biometrics and using password managers with separate passwords for services, especially those that involve sensitive data. That’s a change for the better, since security is important if we are to continue to grow and enhance the use of digital services in our world.

    I think many of the issues with security are because of people near my age, the generation that has grown up as technology has. We’ve embraced and extended the very rudimentary systems that existed before Internet use and mobile devices became widespread. We also learned to build services in a way that gets them up and running without considering security from the beginning. Many of us grew up with computers that were either on or off, without any security implemented. We learned to network with completely open shares, and didn’t bother with access control. This is the same way many developers learned to build SQL Server applications using the sa account, not wanting to spend time learning the (basic) intricacies of SQL Server security.

    As we deal with an ever growing number of data breaches (over a thousand last year), it seems that many of the people working in technology, likely from my generation, still have not learned to build security early into an application. We add security later, after we’ve gotten a prototype or minimally viable product released. In many cases, we might never build security until we suffer some sort of incident. That’s the wrong time to start looking at limiting access.

    With the GDPR being enforced this spring, there will be plenty of pressure on companies to avoid being in the headlines for a data security issue. I’m hoping that customers will continue to put pressure on organizations to adopt better security measures.  Between customers and new legislation in various countries, I’d hope that more managers would understand that security is important and make it a priority for their staff. Most technical people want better security, even at the expense of a little inconvenience. These changing times might just allow us to get our wish.

    Steve Jones

    The Voice of the DBA Podcast

    Listen to the MP3 Audio ( 3.8MB) podcast or subscribe to the feed at iTunes and Libsyn.
  • SSMS 17.4 Vulnerability Assessment

    SSMS 17.5 is out as of February 2018, but the the Vulnerability Assessment (VA) was released in SSMS 7.4

    It seems that the Microsoft tools team is trying to build us better tools that come with the platform. There are good third parties that build tools, such as my employer, Redgate Software, but I am glad that Microsoft is also providing a little more value. This is especially welcome in the area of security.

    In SSMS 17.4, the upgrade came with one goodie: the VA. This is an analysis that will help you determine if you potentially have issues with your instances and databases. This is an assessment of a database, but there are server implications as well.

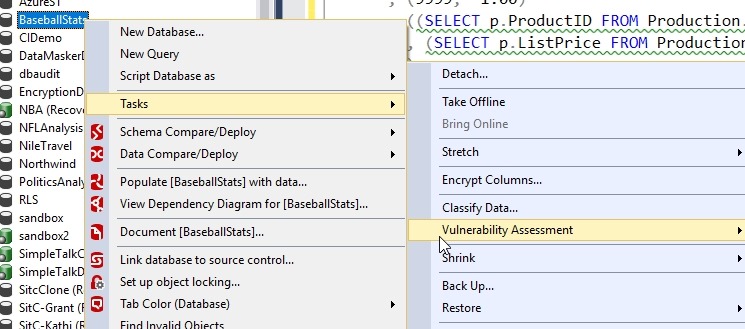
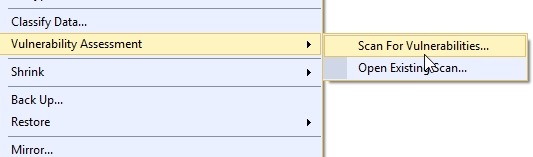
    Once you install or upgrade SSMS, you can right click on a database and choose Tasks, Vulnerability Assessment.

    2018-02-23 17_37_53-

    This is actually a menu of a couple items. You have the choice to run a scan or open an existing scan that you might have saved on your system.

    2018-02-23 17_38_29-SQLQuery4.sql - (local)_SQL2016.AdventureWorks2014 (PLATO_Steve (70)) - Microsof

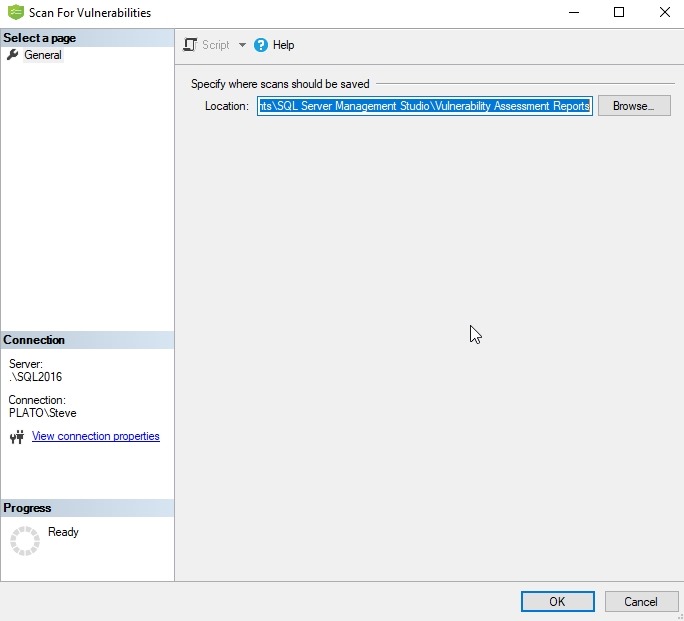
    When you run a scan, a new dialog opens that asks you where to save the scan. You can change the path, and once you click OK, the scan runs.

    2018-02-23 17_39_14-Scan For Vulnerabilities

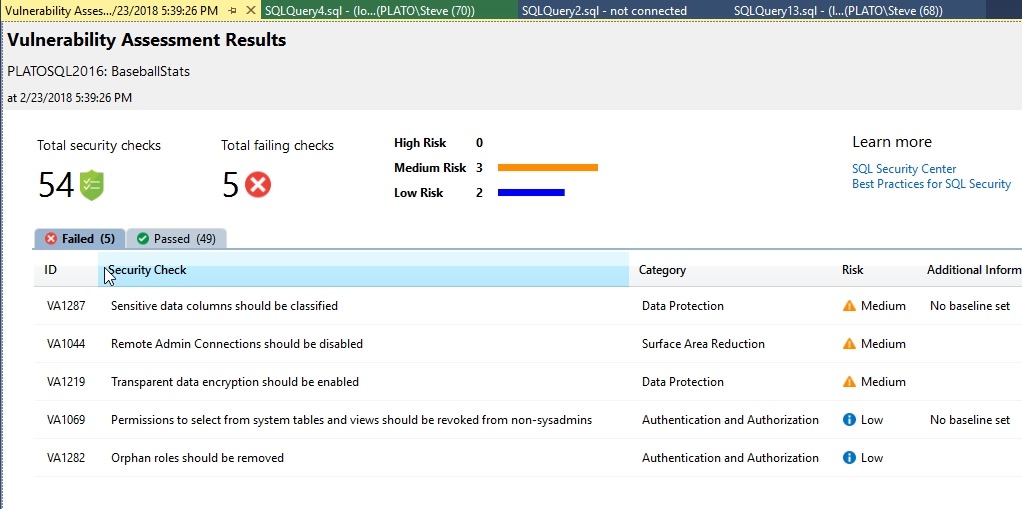
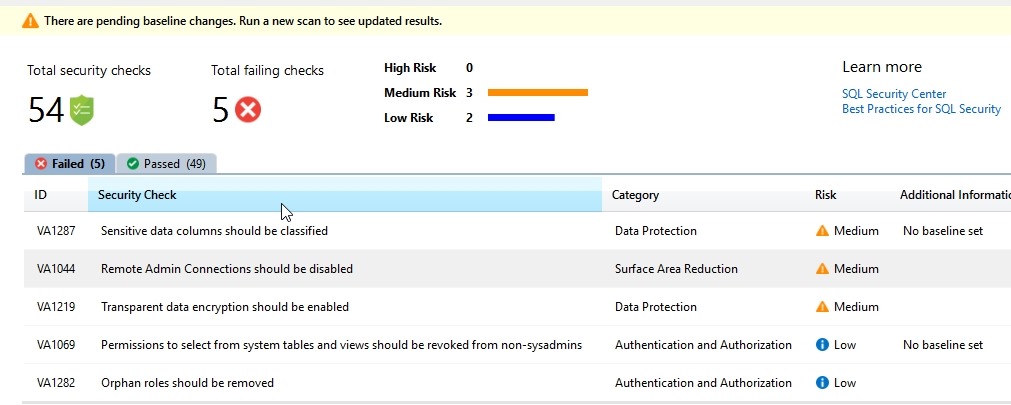
    A new tab opens in the query window space with the results of your scan. This gives you the bad news first. Those items you failed. In my case, I had 5 items.

    2018-02-23 17_50_17-Vulnerability Assessment - BaseballStats - 2_23_2018 5_39_26 PM - Microsoft SQL  

    These items are listed as high, medium, or low risk. I haven’t dug into these too deeply, so I won’t comment on the appropriateness, but look for more information at SQLServerCentral soon.

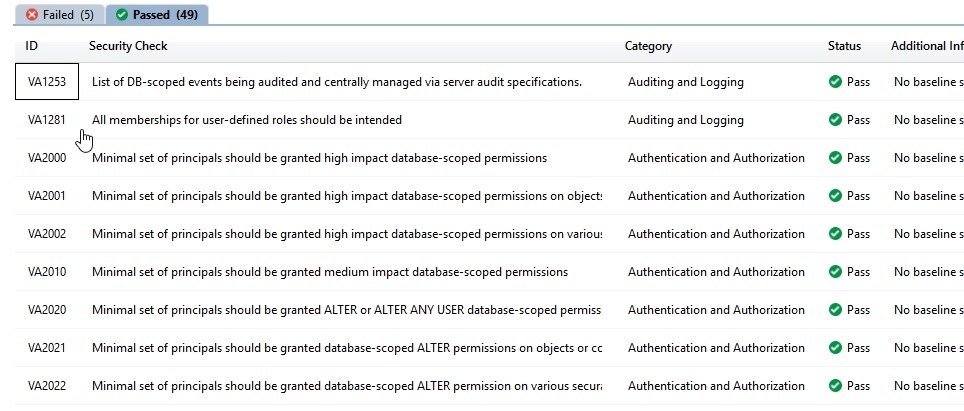
    I did better on the passing side, 49 items.

    2018-02-23 17_50_25-Vulnerability Assessment - BaseballStats - 2_23_2018 5_39_26 PM - Microsoft SQL

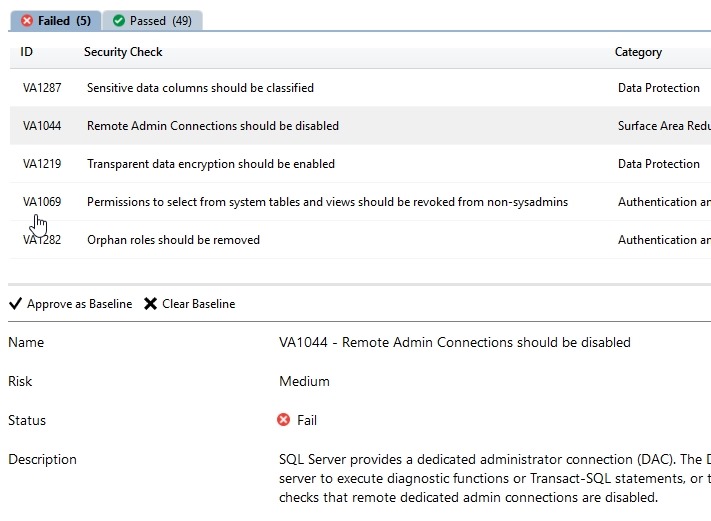
    If I pick an item, I can mark this as approved as the baseline setting. For example, on this instance, I want Remote Admin connections.

    2018-02-23 17_52_32-Vulnerability Assessment - BaseballStats - 2_23_2018 5_39_26 PM - Microsoft SQL

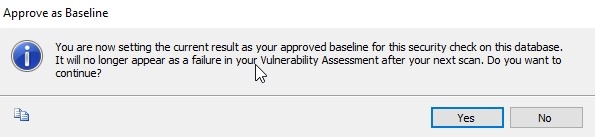
    If I click “Approve as Baseline”, I get a dialog. I’ll say yes.

    2018-02-23 17_52_38-Approve as Baseline

    This item now has a baseline marked, or rather, the absence of a baseline removed. I also get a note that there are changes near the top.

    2018-02-23 17_53_26-Vulnerability Assessment - BaseballStats - 2_23_2018 5_39_26 PM - Microsoft SQL

    If I run a new scan, this issue doesn’t appear.

    2018-02-23 17_54_24-Vulnerability Assessment - BaseballStats - 2_23_2018 5_53_44 PM - Microsoft SQL

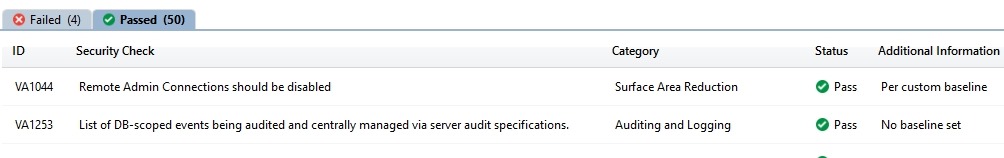
    This is now an item in the Passed tab.

    2018-02-23 17_54_52-Vulnerability Assessment - BaseballStats - 2_23_2018 5_53_44 PM - Microsoft SQL

    This is simple, and perhaps trivial, but having this built into a tool means that you can now start to see if things change. There is likely lots of opportunity to build on top of this and perhaps aggregate data or make it more consumable. Look for other companies to add to this, but for now, it’s nice that Microsoft is adding security help to SSMS.

    You can read more about the Vulnerability Assessment on docs.microsoft.com.

  • Republish: Elevation of Privileges

    It’s another day in the office in the UK and I’m republishing Elevation of Privileges while  I’m stuck in meetings all day.