Tag: security

  • Password Ninjas

    For the time being, passwords are the way that we authenticate users and secure most of our systems. There might be a better system in the future, but for now everyone needs to manage a series of logins and passwords, even if you have authentication for many systems linked through an internal domain or external system, like OpenID.

    I think password managers are almost required these days to manage passwords for most people. I recently ran across an article on ArsTechnica where five security experts were asked how they manage their complex passwords across a multitude of services. Four of these experts use password managers of some sort, though there is quite a variety of them. One actually remembers passwords, though he tries to use proximity tokens and one time passwords when possible.

    Bruce Schneier, one of the security writers I’ve followed for a long time uses Password Safe, which is what I use. However he also likes to use his own advice of long sentences turned into passwords and keeping backups of passwords on physical paper. I don’t like writing down passwords, but if you can keep the paper secure (not stuck on a monitor or under a keyboard), it’s an easy solution to use.

    There are various ports on different operating systems and different methods to keep your files in sync, if you choose to do so. Two others use competing products (1Password and KeePass), but one uses a text file in an encrypted virtual disk image that he keeps on a USB key. I’m not sure I like that, but with proper backups, it’s not a bad solution.

    There is a variety of advice, but overall there’s one thing to keep in mind: security is serious business. All the more so as we use various services more and more to conduct business in our daily lives. Losing a password that you share across multiple services could severely compromise your life. Whatever method you choose, stick to it and be careful in choosing your passwords.

    Steve Jones

    Video and Audio versions

    Today’s podcast features music by Everyday Jones. No relation, but I stumbled on to them and really like the music. Support this great duo at www.everydayjones.com.

    Follow Steve Jones on Twitter to find links and database related items and announcements.
    Steve Jones Windows Media Video ( 14.5MB) feed

    MP4 iPod Video ( 20.2MB) feed

    MP3 Audio ( 3.6MB) feed

    Feeds are available at iTunes and Mevio

    To submit an article, rant or editorial,
    log in to the Contribution Center

  • Hack Resistant

    Security should be on the forefront of every data professionals’ mind. It doesn’t matter if you are developer, administrator, or other position, you ought to be considering the security implications of changes you make to the database. More and more data is being stored in databases, and often it’s moved between databases as well. Whether that’s to data warehouses, or development environments, we ought to be considering security to be more a part of our daily work and process rather than something limited to specific systems.
    Vendors are trying to make systems more secure. I see the encryption capabilities grow with each version of SQL Server, and new features have been added, like TDE, to help technology professionals secure their data. Other vendors have introduced other safety mechanisms, and one caught my eye by claiming to be “hack resistant“. It’s the ZenithVault database says it is practically impossible for hackers to gain access to storage systems and steal confidential information. It supposedly does this by “data splitting”, moving parts of data onto separate servers.
    It sounds like a good solution, in the same way that TDE is a good solution. If someone is able to access your physical files, they won’t be able to read the data in them. That’s a good precaution, and it works well in TDE’s case (I can’t speak for ZenithVault), but it’s also not hack resistant.
    The biggest hacking problem that I see in the world today is with SQL Injection. Since legitimate accounts can access your database, often through web-based front ends, and SQL Injection uses these same accounts to access data, none of the encryption and security capabilities you set up protect you. None of these items come into play when you have code that allows hackers to inject their own commands through your existing application, web based or not.
    Secure coding is important, and it’s something that we should all require and practice as we build software. Your application might not access secure data today, but that might change in the future.
    Steve Jones

    The Voice of the DBA Podcasts

    We publish three versions of the podcast each day for you to enjoy.

  • Who’s Got Your Data?

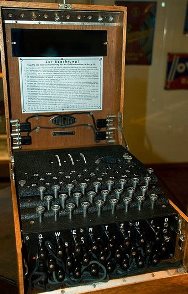
    enigmaThe headlines lately have been filled with the plight of Edward Snowden, along with his disclosures on how the US National Security Administration (NSA) has been gathering, cataloging, and examining all sorts of data about people in the world. It’s not just terrorists, criminals, or anyone suspected of illicit activities, but also many ordinary people that may not feel they should have been subjected to this level of surveillance. Whether you think this was a proper way to disclose this information or not, there’s a separate issue here.

    We are producing a tremendous amount of data about ourselves all the time. There are so many ways in which companies can gather data points about us, often with logging activity that we might not find intrusive. Our houses produce logs of electrical activity along with the various types of services we might use (water, trash, etc.). We use cell phones, whose locations and usage are recorded, and we often use on line services for mail, research, entertainment, and more that all produce logs of our activities. Purchases on line are stored, and purchases off line might be stored if you use any type of loyalty card. I can imagine it not being long before any card purchase can be linked to the actual items themselves, regardless of whether you want this to occur.

    We can add in any services we use that store data in the cloud, from physical activity to medical information to even your location from status updates. While much of this data is stored separately, and not necessarily aggregated, that might not be the case in the future. The government could potentially request this data, which is unnerving to me, but what is more disconcerting is the idea that businesses might engage in complex deals to share much, or all, of your data without you knowing about it. This could be under the guise of providing better services, which makes sense, but that’s not what concerns me.

    What concerns me is the lack of care that so many companies take with our data. It’s lots constantly, and the more data that might be shared between companies, and need to be transformed and loaded into new data warehouses, the more people that will touch this data. And the more developers that will have copies of it on their laptops as they build new applications. It’s scary to think about the lack of control we have, and now many mistakes will be made in the future.

    I wish I had a good suggestion on how to improve the situation, but I don’t. However I do think disk encryption, for all machines that touch data, is a good place to start.

    Steve Jones

  • More Data Security Issues

    Employee issues are a big problem for IT security.
    Employee issues are a big problem for IT security.

    Insiders and human frailty are still a big problem in data security, according to a new study from Symmatec. Along with system issues these account for two thirds of data breaches. I suspect system issues means misconfiguration and poorly written code (from a security standpoint), though I can’t be sure there aren’t other factors that contribute. What’s disconcerting is that employee behavior problems seem to be rising.

    I think this is partly the result of attitudes and a lack of loyalty and respect from many companies towards their employees. It seems that job dissatisfaction is on the rise, and coupled with a lack of employment security, this makes it easy for some people to ignore regulations, not bother securing their systems, or even copy internal data themselves.

    I don’t know how we change the insider problems without fundamental employer/employee cultural changes. I’m not confident those will change in the short term, and I suspect next year’s report might look similar to this one. I do know, however, that we can each to a better job by learning more about secure coding, secure installation, and encryption. Many of these topics aren’t that hard to understand or even implement, but they do require some practice to build habits and become comfortable with the technologies and processes.

    Security is looking like a constant challenge for those of us working with technology for the foreseeable future. Learning more about how it works, and building the habits to implement it smoothly, in all our systems, or the challenge we should take on for ourselves.

    Steve Jones


    The Voice of the DBA Podcasts

    We publish three versions of the podcast each day for you to enjoy.