Over the last couple of years I’ve gotten myself down to two small, carry-on bags for most of my trips. It has allowed me to save time in and out of the airport, and cut down on a lot of hassles from frequent trips (I flew on 18 round trips last year).
One of the ways I’ve done this is with a couple dedicated bag: one for clothes/shoes and one for the laptop and supplies. I don’t ever really unpack them, and I just move clothes in and out when I go. That always has me a little nervous as I am counting on things to be in the bags, but it’s worked for a dozen trips lately because I keep spares of all my supplies in the bags, replacing them as needed, but not using them for other purposes.
However that can come back to bite you. I did have a trip last year where I left my presentation remote at home since I’d been using it to practice and hadn’t put it back in my bag before I left. Fortunately that’s a minor inconvenience and not a major hassle.
I leave for the UK on Saturday for my annual visit to the Red Gate office in Cambridge, and I need to pack for a week. I’m hoping to slip in enough clothes to go with just my two bags, but we’ll see. I’ll also use this chance to double check I have everything packed I need since replacing stuff in another country is less than exciting to me.
One of the problems with hashing is that you can have collisions from values that are not very similar. This means that if you are using hashing as a way to identify similar values, you need to make further checks with the original data after the hash matches are gathered.
This post will show a few examples of the collisions that can occur if you use the CHECKSUM() or BINARY_CHECKSUM() functions.
Note that these two values are the same as far as the checksum hash goes.
If we switch to BINARY_CHECKSUM(), we can get similar results.
-- binary_checksum is no better
declare
  @i varchar(200)
, @j varchar(200)
, @k varchar(200);


select @i = 'LE'
select @j = 'Ou'
select @k = 'MU'

select
  Plaintext = @i
, BINARY_CHECKSUM(@i)
UNION ALL
SELECT
  Plaintext = @j
, BINARY_CHECKSUM(@j)
UNION ALL
SELECT
  Plaintext = @k
, BINARY_CHECKSUM(@k)
GO
While these two functions can be useful, you do have to be careful with the results. A matching hash from these functions does not mean that the source data is the same.
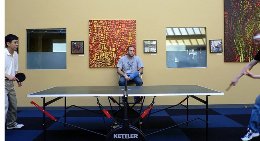
In a few jobs, we had a ping pong table at work and it was a great place to take a 10 minute break from work.
I used to come into work, get some coffee, sit in a cube, put headphones on, and then spend my day stuck in the world of SQL Server. Solving problems, working on trouble tickets, analyzing performance and more. An occasional meeting interrupted me, and an empty coffee cup interrupted me more, but for the most part I worked as a DBA with headphones on, doing my job. However I wasn’t perfect. There were times that I surfed the web, looking for news, answering questions on forums or more. Add this to the conversations with co-workers about non-work topics and it’s clear that 8 hours at work isn’t 8 hours of work.
I’m not alone, and most of my co-workers engaged in other sorts of distractions as well. We weren’t alone either, and this survey from Salary.com shows some interesting results. Many people spend time on the Internet on non-work tasks, and I think that’s OK. I also think it’s not much different from the pre-Internet days of work. Smoke breaks, random walks around the building, water cooler time, I think some people would be surprised how much time they spend away from “work” if their movements and efforts were tracked by the minute.
As humans, we aren’t going to focus on a single task for a long period of time unless it doesn’t require much thought. For anyone that has to think, however, distractions are necessary over time. Extreme concentration in one area can easily leave us locked in to a particular solution, creating tunnel vision. It’s also hard, and requires some downtime to recharge. That downtime at work can easily come from a few distractions that let your mind wander. The best people I’ve worked with often had short breaks spread in their day. A game of table tennis, playing a song on a guitar, a short conversation, or even working with a co-worker on some problem unrelated to their job. What looked like a waste of time didn’t seem to affect their productivity.
Not everyone handles the freedom well, and plenty of people get distracted to the point of being unproductive. However eliminating all distractions doesn’t necessarily make them more productive. They’ll just find some other way to distract themselves. Great employers look to help people learn to manage themselves better, shortening breaks, learning to tackle problems as a challenge, and perhaps learning to become better at their craft by using some break time to learn more.
Steve Jones
The Voice of the DBA Podcasts
We publish three versions of the podcast each day for you to enjoy.
To me, certificates are the best way to secure communications and be aware of what’s allowed and what isn’t.
One of the things that I think has been most disappointing to me in technology over the last few decades is the lack of progress is managing security keys and certificates. There hasn’t been a really good method designed that works well at scale for disparate organizations.
Recently at the DevConnections conference, I saw a talk where Mark Minasi talked about the future of tablets and smartphones, where he mentioned the idea that we will use many devices in the future that don’t necessarily need to connect to the domain inside a company. They’ll still authenticate, but with certificates.
That would be the ideal situation for me, a world where we individually have multiple certificates that identify us, and allow us to have secure communications, layers of security for different purposes, and a way to easily revoke, change, and add new certificates as needed. I’d be able to use easily manage certificates across devices to provide some level of authentication.
As we move to the deep intermixing of user and company devices, it does start to make sense that we consider using a more ad hoc authentication scheme that can be deployed in a more distributed fashion, rather than the monolithic, authenticate to the domain completely or not at all, scheme we have now.
I don’t have a solution worked out, but I know there are some very smart security people out there and I’d hope that they are working on a variety of solutions that will increase the security we have, while allowing us lots of flexibility.
Steve Jones
The Voice of the DBA Podcasts
We publish three versions of the podcast each day for you to enjoy.