Author: way0utwest

  • Adding SQL Change Automation to Jenkins for Database CI

    In a previous post, I explained how to get Jenkins running in a container for your local CI work. In this one, I’ll expand on the process for database CI with a quick look at getting the SQL Change Automation plugin added to Jenkins

    The first step here is to click the Manage Jenkins menu item from the home page.

    2019-07-27 17_14_17-Manage Jenkins [Jenkins]

    This gives you a number of items on the right. Scroll down and you’ll find the Manage Plugins option.

    2019-07-26 15_41_18-Manage Jenkins [Jenkins]

    Once you click this, you see a list of the installed plugins with updates in the right. You also see a few tabs for managing and adding plugins. Click over to the Available tab for plugins that you can add, but don’t have installed.

    2019-07-26 15_41_29-Update Center [Jenkins]

    In the upper right is a Search box. I entered “redg” and you quickly see the list shrink to the one you want: the Redgate SQL Change Automation plugin.

    2019-07-26 15_41_35-Update Center [Jenkins]

    Check the box next to the plugin (in the Install column) and then click “Install without restart”. I restart isn’t needed in this case to get the plugin to work. Once you click this, you will see the plugin status appear.

    2019-07-26 15_41_46-Update Center [Jenkins]

    It should install quickly and let you know it’s done. I did this 4 or 5 times and every time it just worked.

    2019-07-26 15_43_32-Update Center [Jenkins]

    At this point, you can add this plugin to your builds. When you have a project, this will be one of the possible options. In a future post, I’ll look at actually performing a build with the SQL Change Automation Plugin.

    There are other posts in this series:

  • A Memory-Optimized Roundup – T-SQL Tuesday #117

    The summary from my fourth T-SQL Tuesday hosting for #117. This time I was scrambling a bit, but since I’ve worked with a few customers in the last year that use MOT tables, I thought this might be a good topic.

    Either everyone is on vacation or not many people think about them. Or maybe they aren’t interesting. In any case, here’s the roundup.

    Rob Farley has a win with user defined table types that are used in MOT objects. Never knew this was a possibility. Extra points for mentioning source control and DevOps.

    Kevin Chant notes he studied them for his MCSE, but hasn’t really found them useful. Mostly because of older versions and restrictions on the feature. Kevin likens this to filtered indexes, which are a nice feature, but rarely used.

    Jess Pomfret writes about some of the limitations for a feature she hasn’t used. A good summary of what they are, but don’t let her turn you off of the feature. It has its place.

    Ken Fisher has a few notes about why he hasn’t used them. Not enough memory in his systems, older versions, and he doesn’t write the code. Apparently I’ve given him some things to think about and play with, and I’m sure I’ll see more blogs from him soon.

    Johan Ludvig Brattås explains how he improved performance with a MOT table.

  • IT Staffer Fired

    In the early 2000s, it seemed that many companies were hit with a rash of virus attacks on their networks. Certainly the SQL Slammer worm affected many of us, and it was a memorable week for me. I returned from vacation to get a call late on Sunday night informing me of issues. I spent a long work working with network people and Microsoft to rid our (shut down) network of the worm, a difficult process with a wide deployment of MSDE instances installed in non-standard locations.

    Not long after this, we had another virus invade our network and shut down systems. This was due to a high level manager clicking on an attachment in email, which spread issues to (far too) many others inside the company. Another long night for me patching and cleaning systems, and one where I questioned how someone could be fooled.

    In the last year, a similar rash of incidents have spread around various organizations, this time with ransomware instead of viruses. One Florida city government was hit, with an IT worker being at fault for opening a document they received in email. The result? The city paid a ransom and the employee was fired.

    Is this fair? I’ve seen the Twitter mobs and rapid comment trolls condemning and praising both sides. It appears many people rightly think someone clicking on unknown attachments should be fired, while there is no shortage of others that understand that humans get fooled and termination is too harsh.

    Personally, I don’t know what to think. While most phishing and spam is poorly written, and I often check headers and easily see these notes for what they are. I have seen some very sophisticated and incredibly deceitful emails that might fool most of us.

    If you have a privileged account, you better be really careful about opening any attachments from email. You shouldn’t download pictures by default except from whitelisted senders, and you might even want to stop doing that. Who knows if your co-worker or business partner got fooled.

    It’s disconcerting though not unexpected. Perhaps this person was at fault, perhaps it was  mistake. Being fired is never fun, and all of us should be a little worried about this if we’re not careful.

    Steve Jones

    Listen to the podcast at Libsyn, Stitcher or iTunes.

  • Actual Kubernetes

    This post continues looking at my process of learning more about Kubernetes. I’ve been working through the 50 days of Kubernetes (K8s). I completed the first 3 sections (Days 1-15). This starts the look at Days 16-20

    Disclosure: I actually ran a kubenetes cluster in Azure Kubernetes Services (AKS), but just using scripts from Andrew Pruski.

    Starting to work with Kubernetes

    Setting up Kubernetes is cumbersome. The setup and configuration is a little daunting but this look gives you a quick start. Microsoft is working with Katacoda here to run some things in the browser. I’m guessing they have some virtual environment you can use to get things running here.

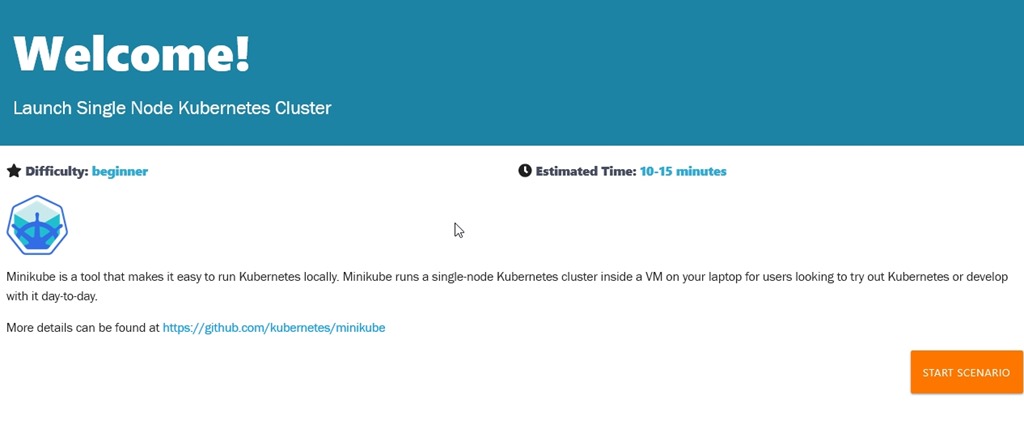
    When clicking the Day 16, we start with the welcome course that launches a single node Kubernetes Cluster.

    2019-07-09 15_21_53-Microsoft Edge

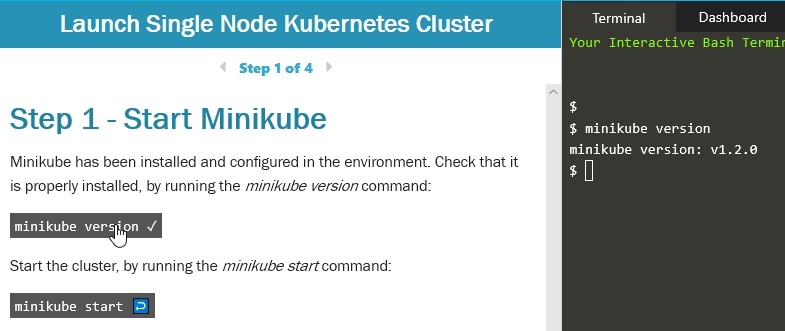
    When you start the scenario, you get the course on the left and a terminal on the right. If you click a section of code (like minicube version), it will run this in the terminal.

    2019-07-09 15_22_42-Microsoft Edge

    I typed most of the commands to get a feeling for the work. It’s definitely some work here, and lots of commands. I think I’d prefer to let Azure or AWS run this for me, but I guess I’ll still admin some of it.

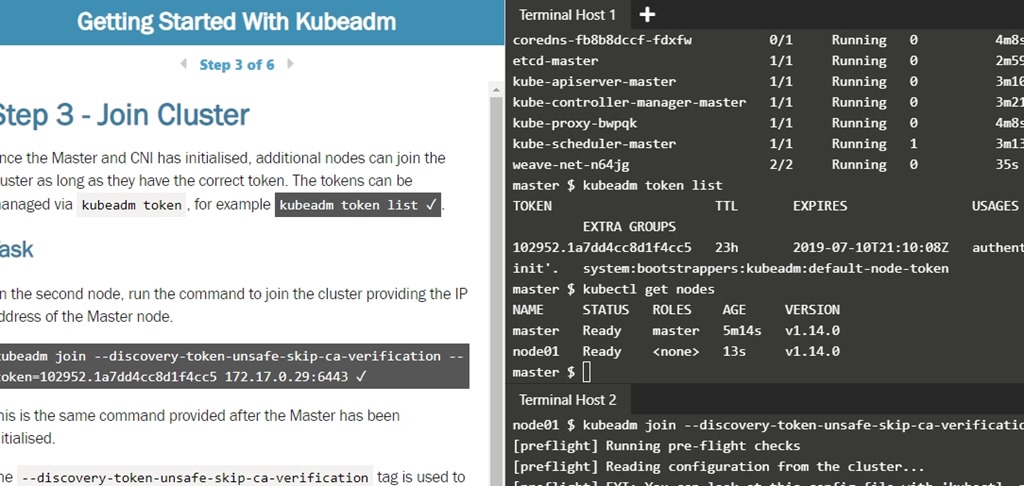
    The first course gets you a cluster with minikube. The second course lets you set up a two node cluster, which is a little more interesting. After all, the idea here is that you want a whole series of machines to act as a cluster of nodes. The process to join nodes is with a token, at least here it is. There can be other authentication if you really do this.

    2019-07-09 15_16_26-Getting Started With Kubeadm _ Kubernetes _ Katacoda

    Continuing through the course across a few days, I got a feeling for how to join new nodes and change the configuration of the Kubernetes cluster. For the most part, I have a general idea of how to set up new nodes, access tokens, etc. While I don’t really know how or why to make changes, I do at least understand what changes are possible.

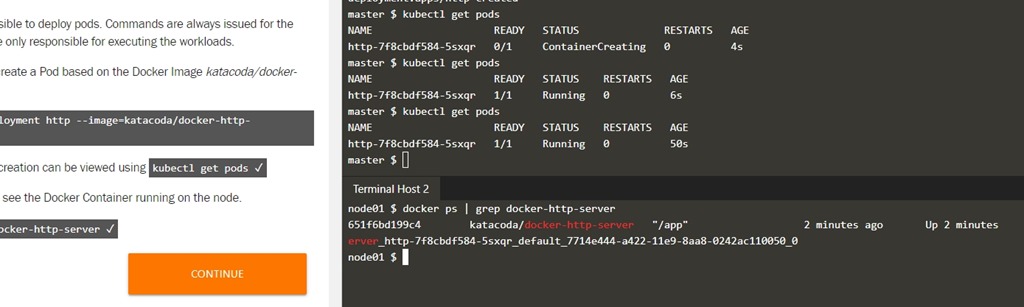
    I did run the “get nodes” or “get pods” a few times, seeing the different messages as new containers/pods were being created, noting the delays as things are deployed. I also learned that the containers distributed on the nodes are shown under the Docker command CLI. That is interesting and unexpected to me, though it shouldn’t have been.

    2019-07-11 15_28_05-Getting Started With Kubeadm _ Kubernetes _ Katacoda

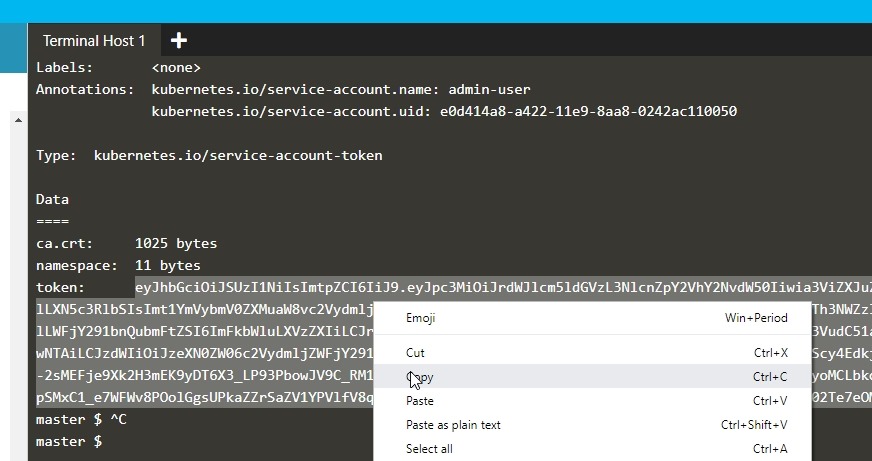
    One thing to be aware of when trying to access the dashboard is that the token copy needs to be with a right click. At least for me, CTRL+C didn’t work.

    2019-07-11 15_30_25-Getting Started With Kubeadm _ Kubernetes _ Katacoda

    I even re-ran a few deployments, adding new pods and web servers to the deployment, which was interesting to me.

    Working through scenarios

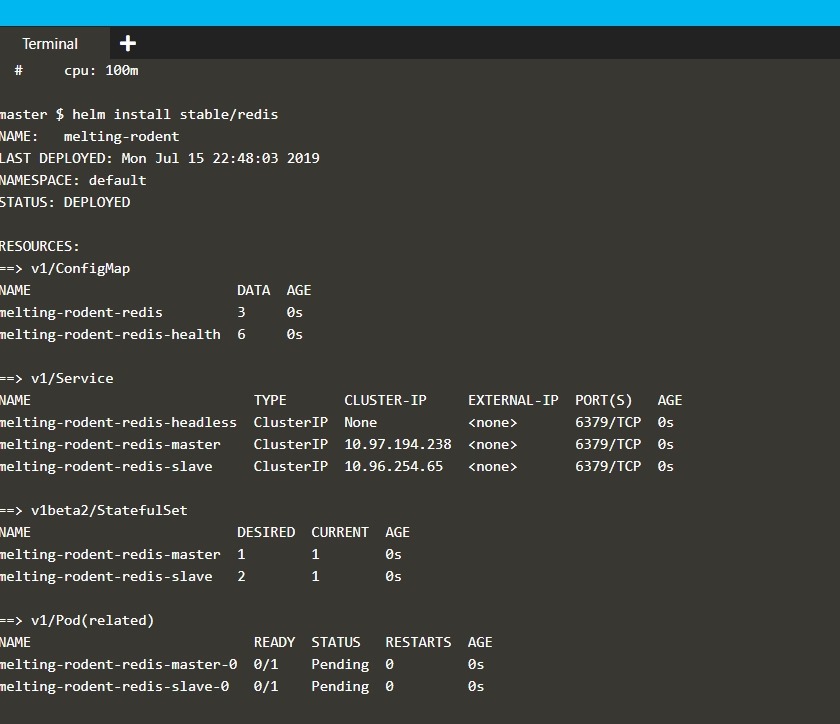
    In this course, there were 17 different scenarios. Adding volumes, networking, stateful services, building deployments, etc. Even using Helm.

    2019-07-15 16_48_21-Helm Package Manager _ Kubernetes _ Katacoda

    For most of these, I’d click the code to run it, and read through the results, seeing how this works. The actual details of creating a secret and retrieving is aren’t likely things I’ll remember, More, I’m just trying to understand how things work.

    The different scenarios do give you an idea of the breadth of Kubernetes capabilities. Certainly if you need to do these things, it would to go through the course, maybe even changing around some parameters. I’d suggest you go through this if you’ll be deploying systems and applications.